Solutions / Google Workspace
Google Workspace security audit against CIS and CISA SCuBA
With read-only admin scopes delegated to a service account, AQIRA inventories users, groups, admin roles and connected OAuth apps, reads sign-in, Gmail, Drive and audit settings, and validates sharing and forwarding to benign proof.
- You provide
- A Workspace tenant
- Intensity
- Standard
- Scored against
- CIS Google Workspace, CISA SCuBA (GWS)
- Plans
- On Enterprise, with 2 tenants (Google Workspace or Microsoft 365), or 1 tenant as an add-on to Premium. Compare the plans
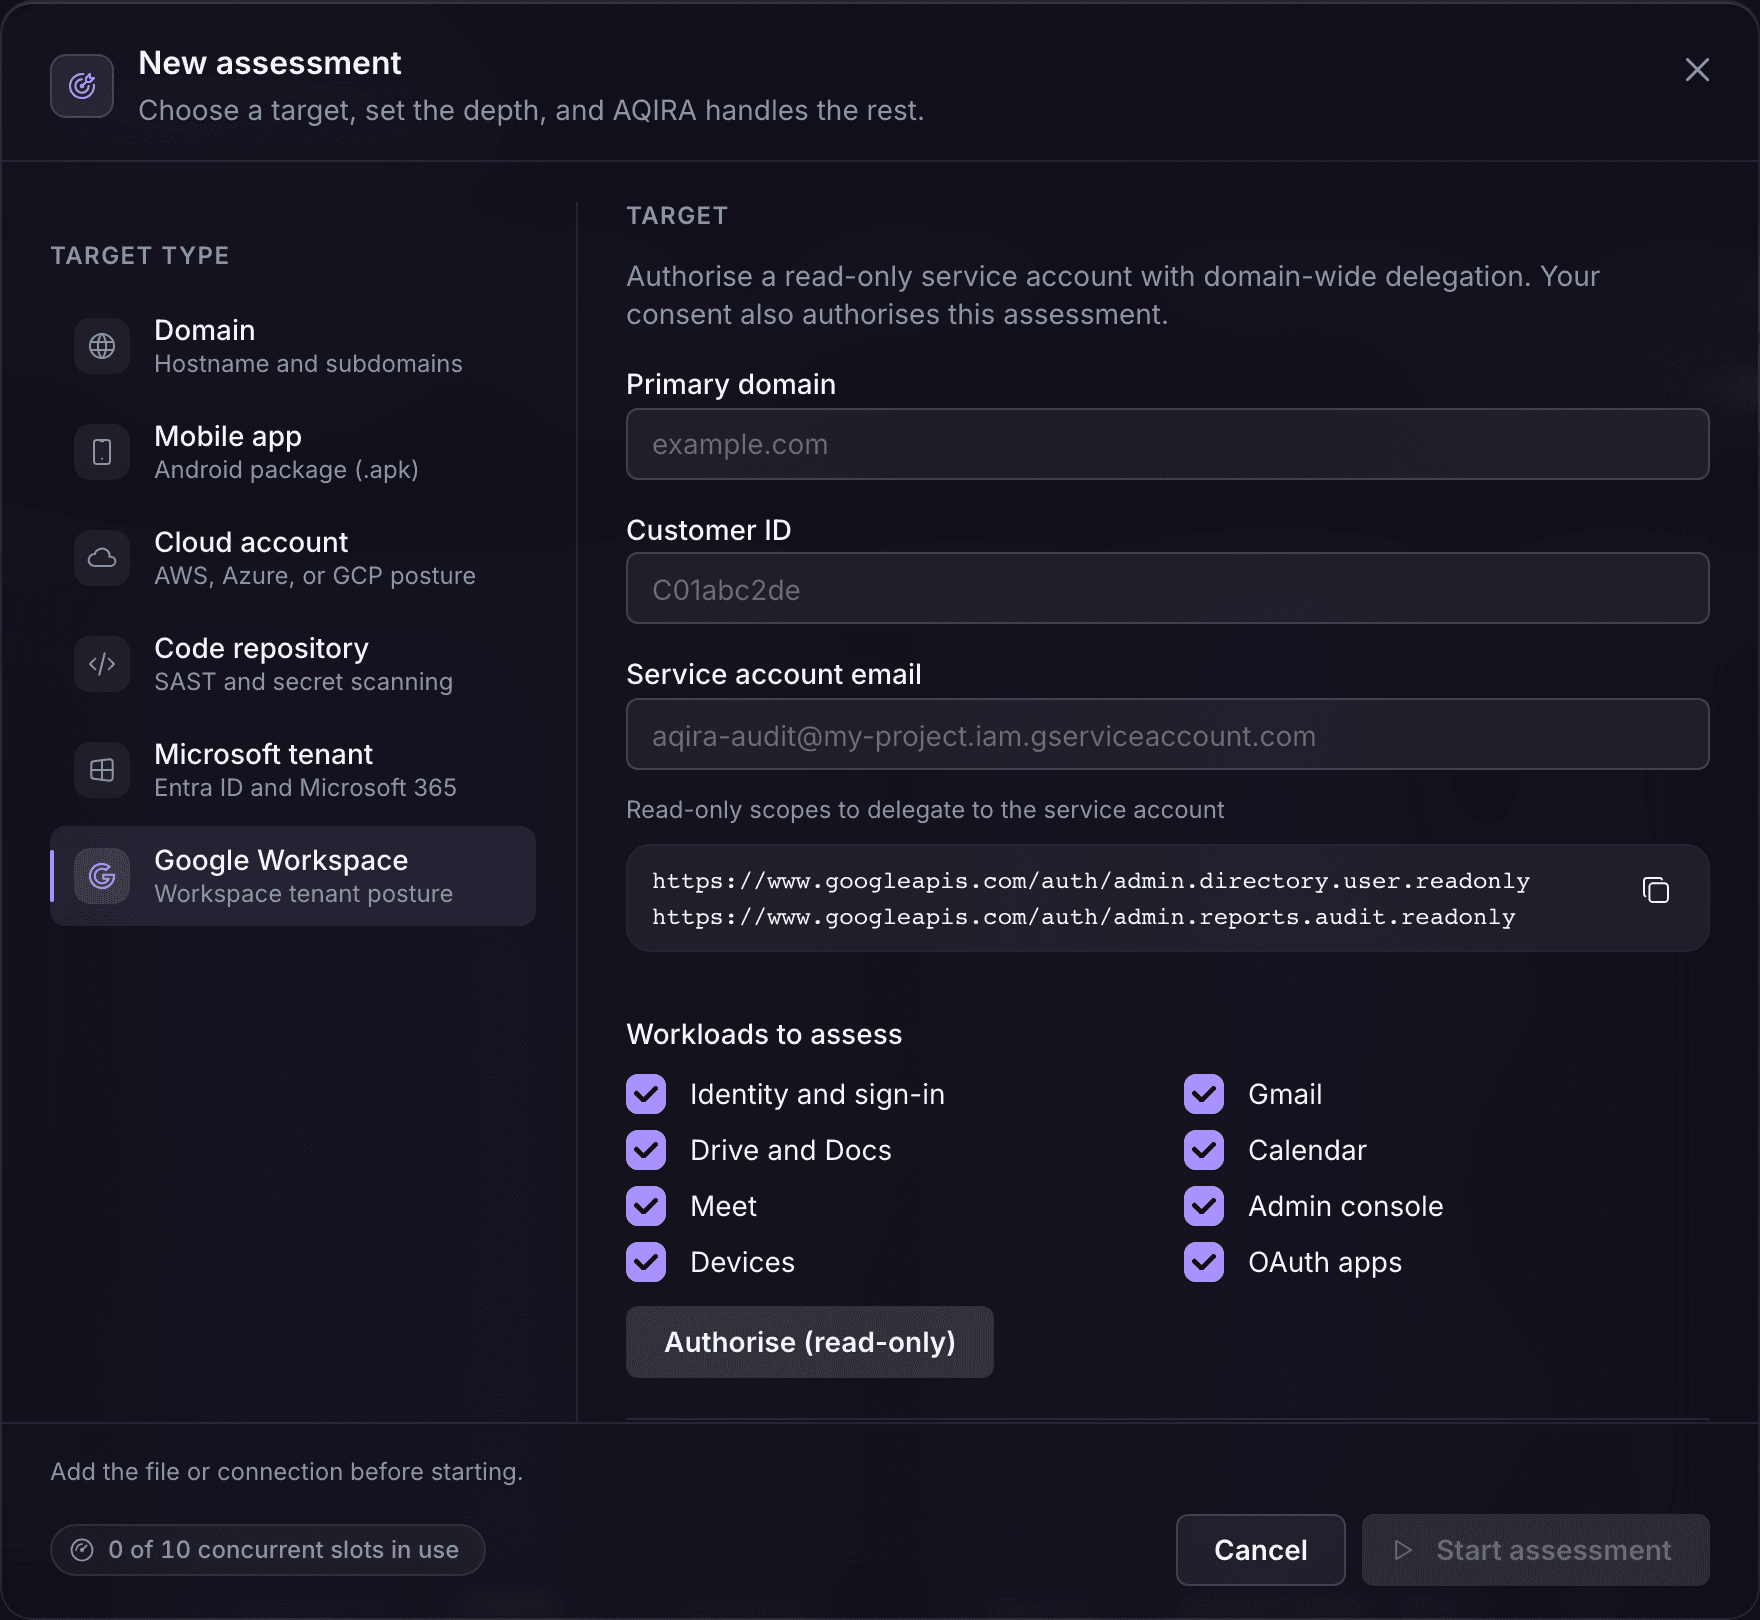
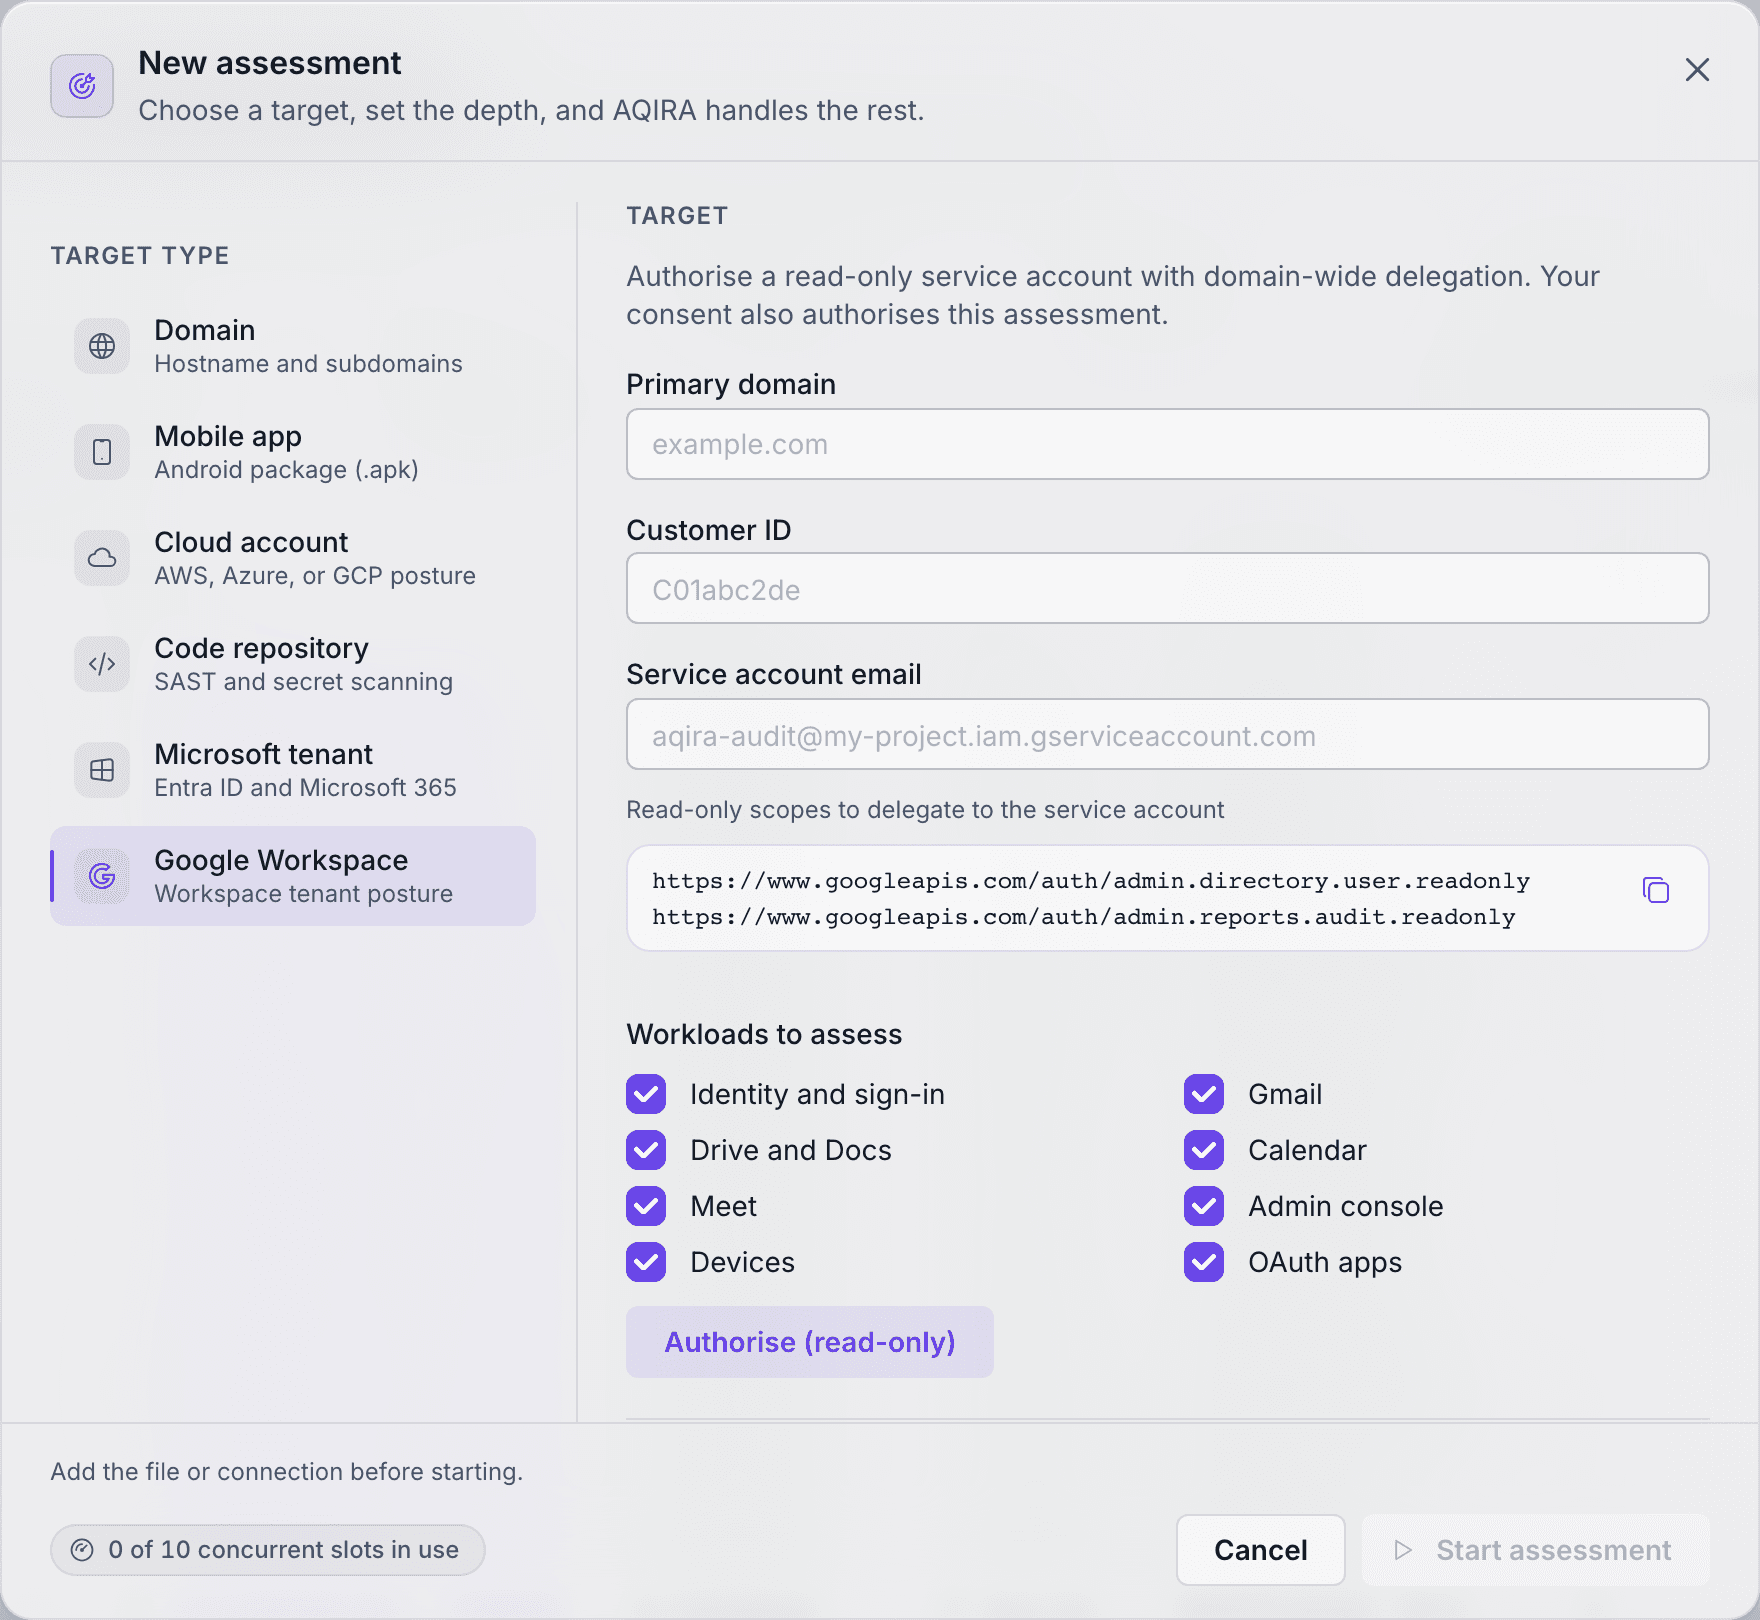
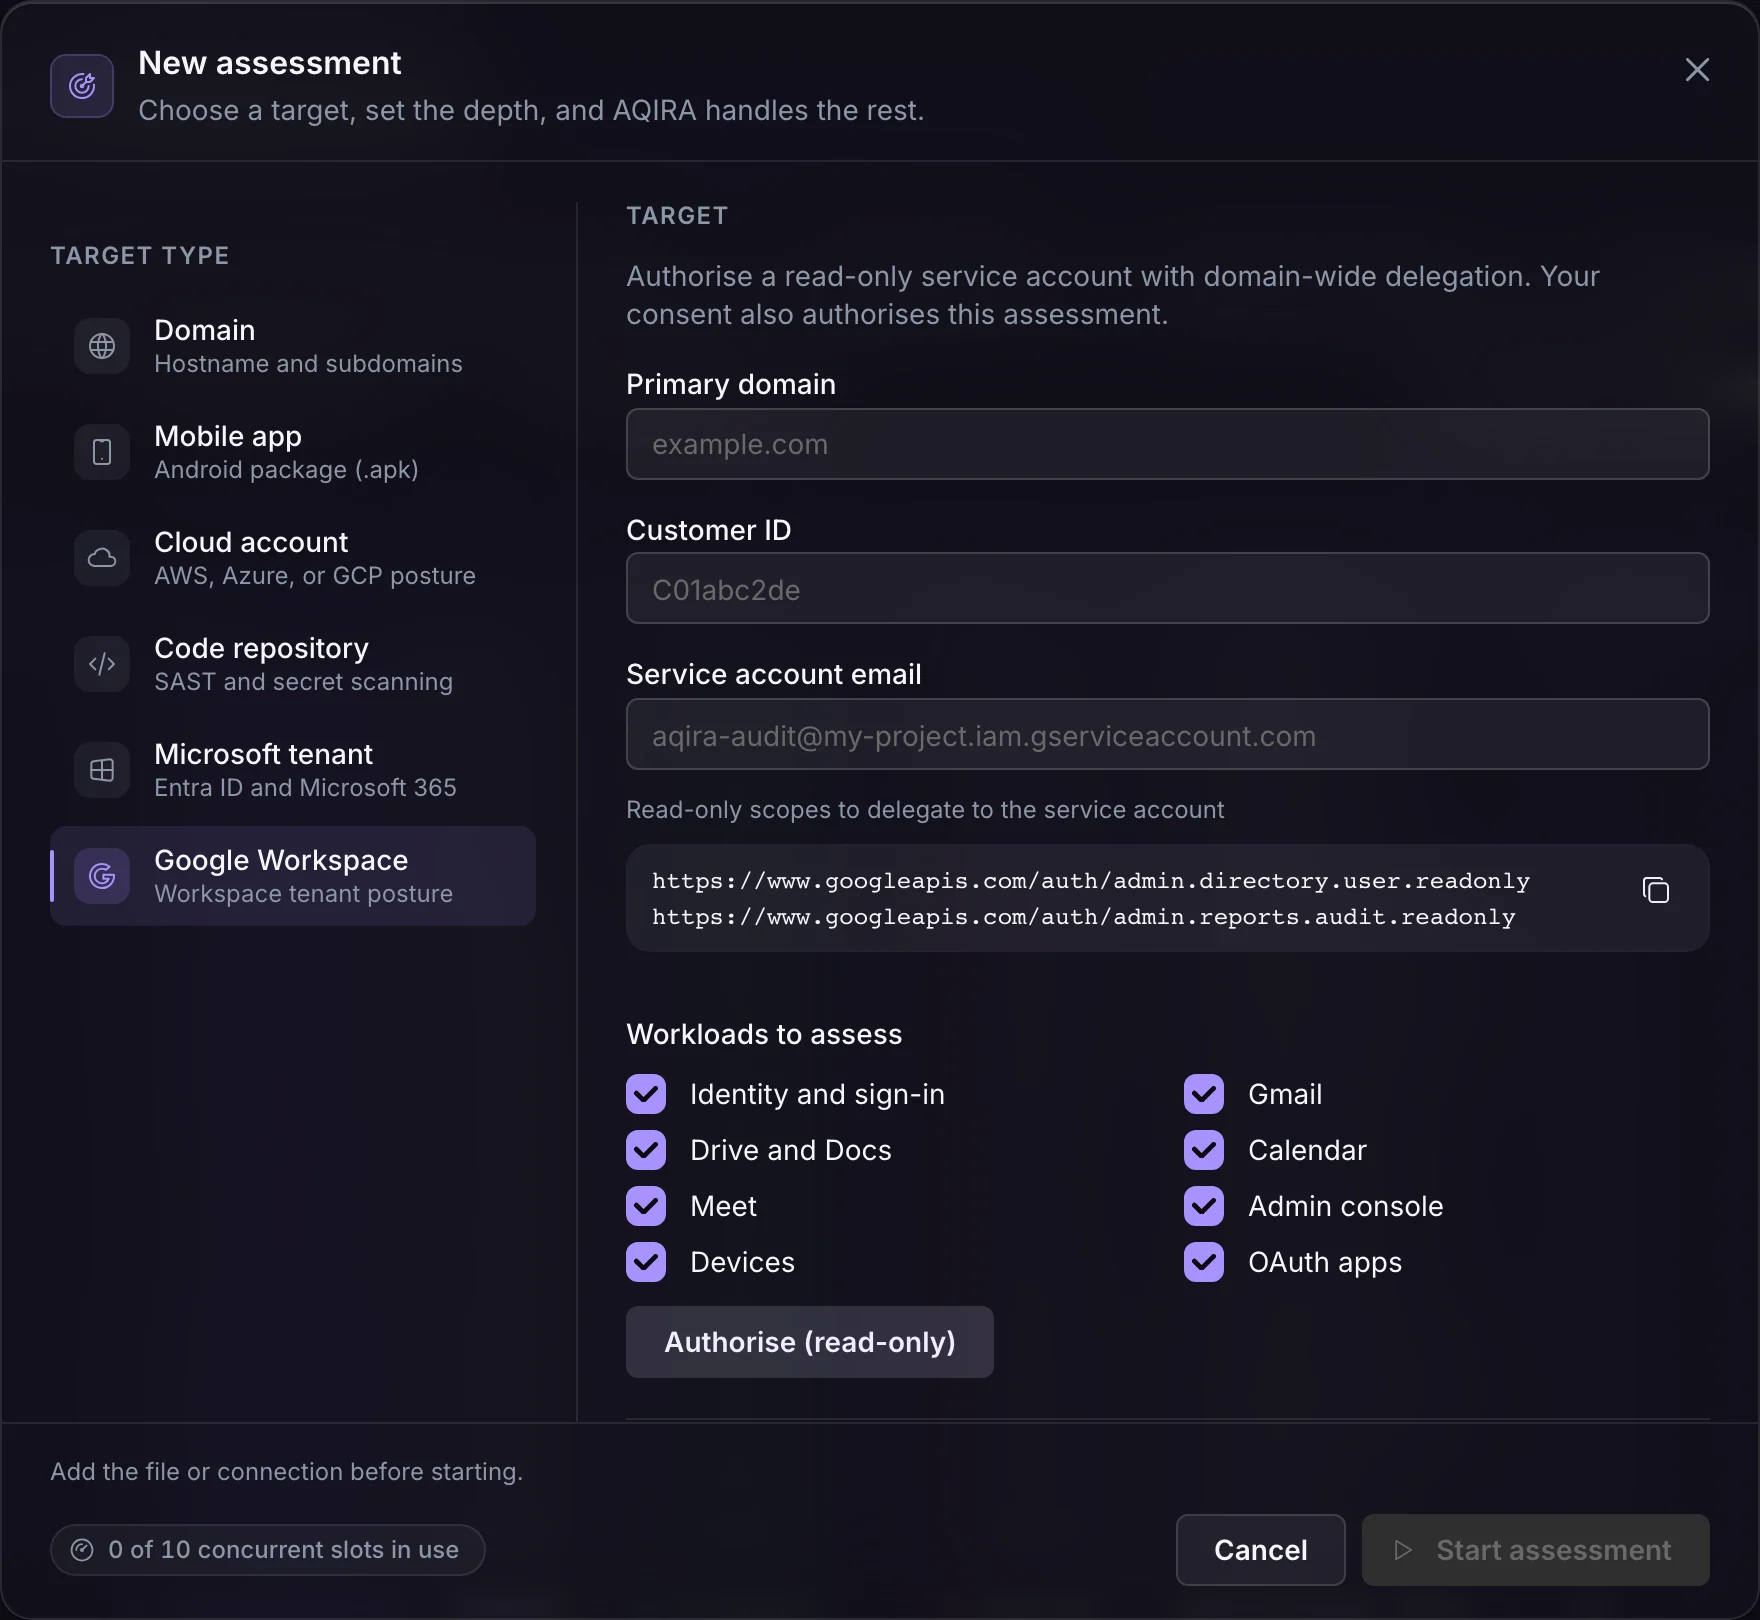
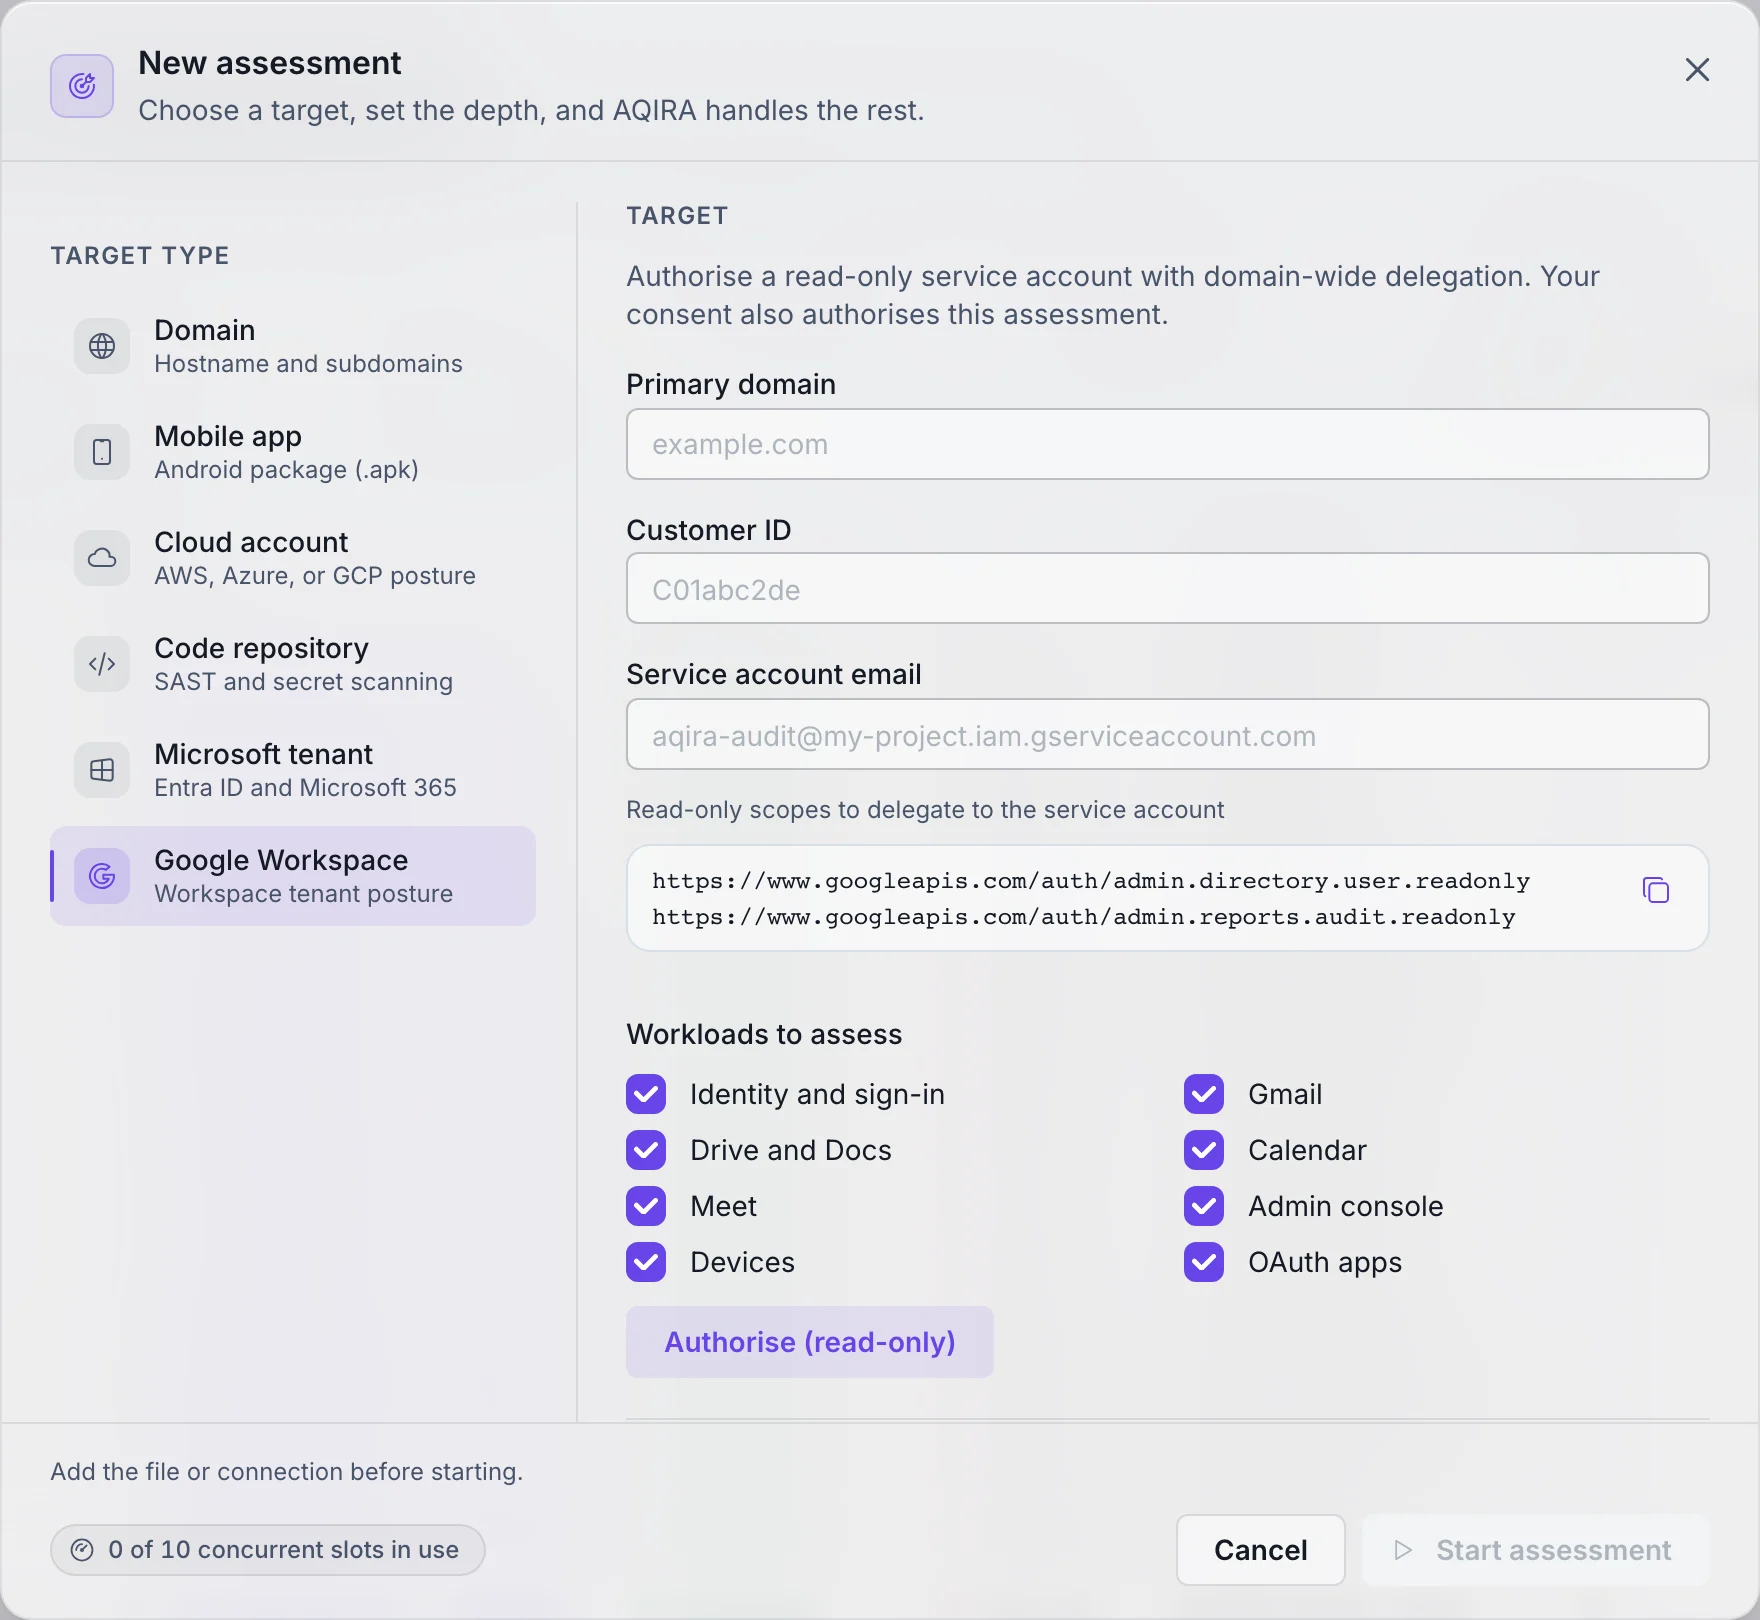
What you hand AQIRA
On a Workspace tenant, the New assessment step asks for the following.
- You provide
- A service account with domain-wide delegation of read-only admin scopes, and the workloads to assess, from sign-in to Gmail, Drive and OAuth apps.
- Access
- Read-only scopes are delegated in your own admin console. Consent also authorises the assessment.
- Authorisation
- The assessment starts only once the operator confirms:
I authorize a read-only assessment of this Workspace tenant.
- Intensity
- Standard. Active testing with safe, non-destructive proofs of concept.
What each input's access allows, and how AQIRA keeps it to the least it needs, is on the security page.
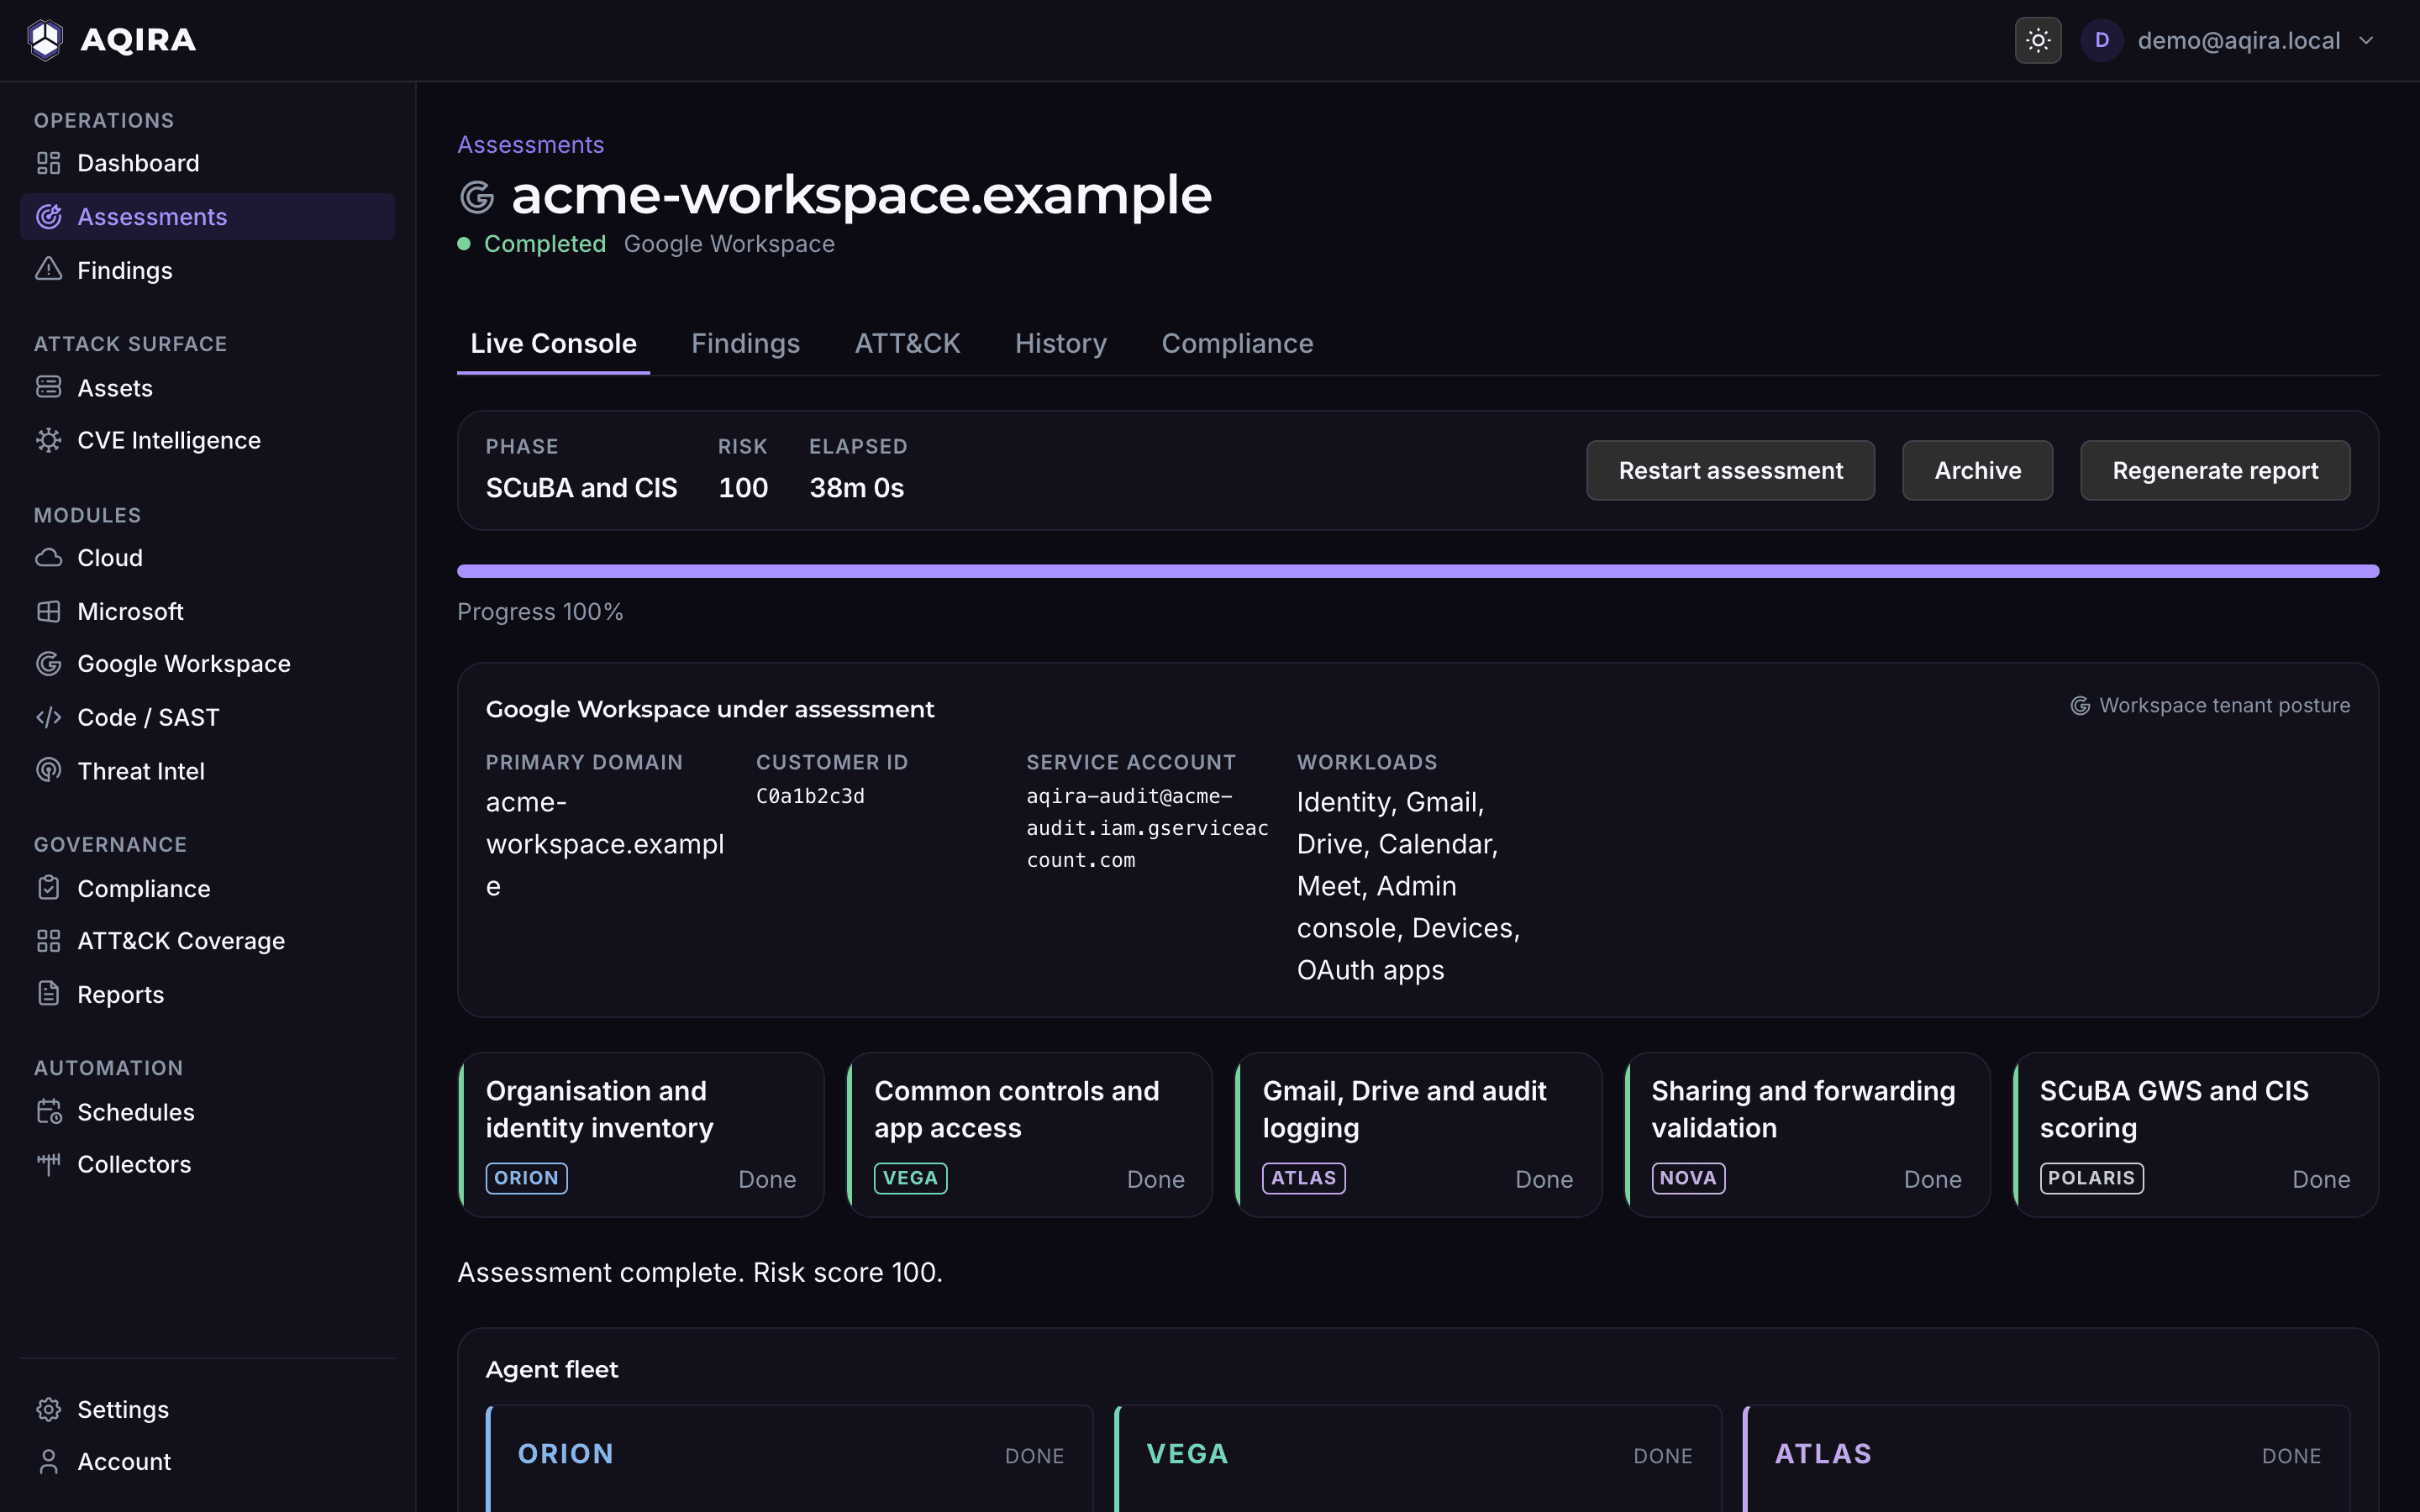
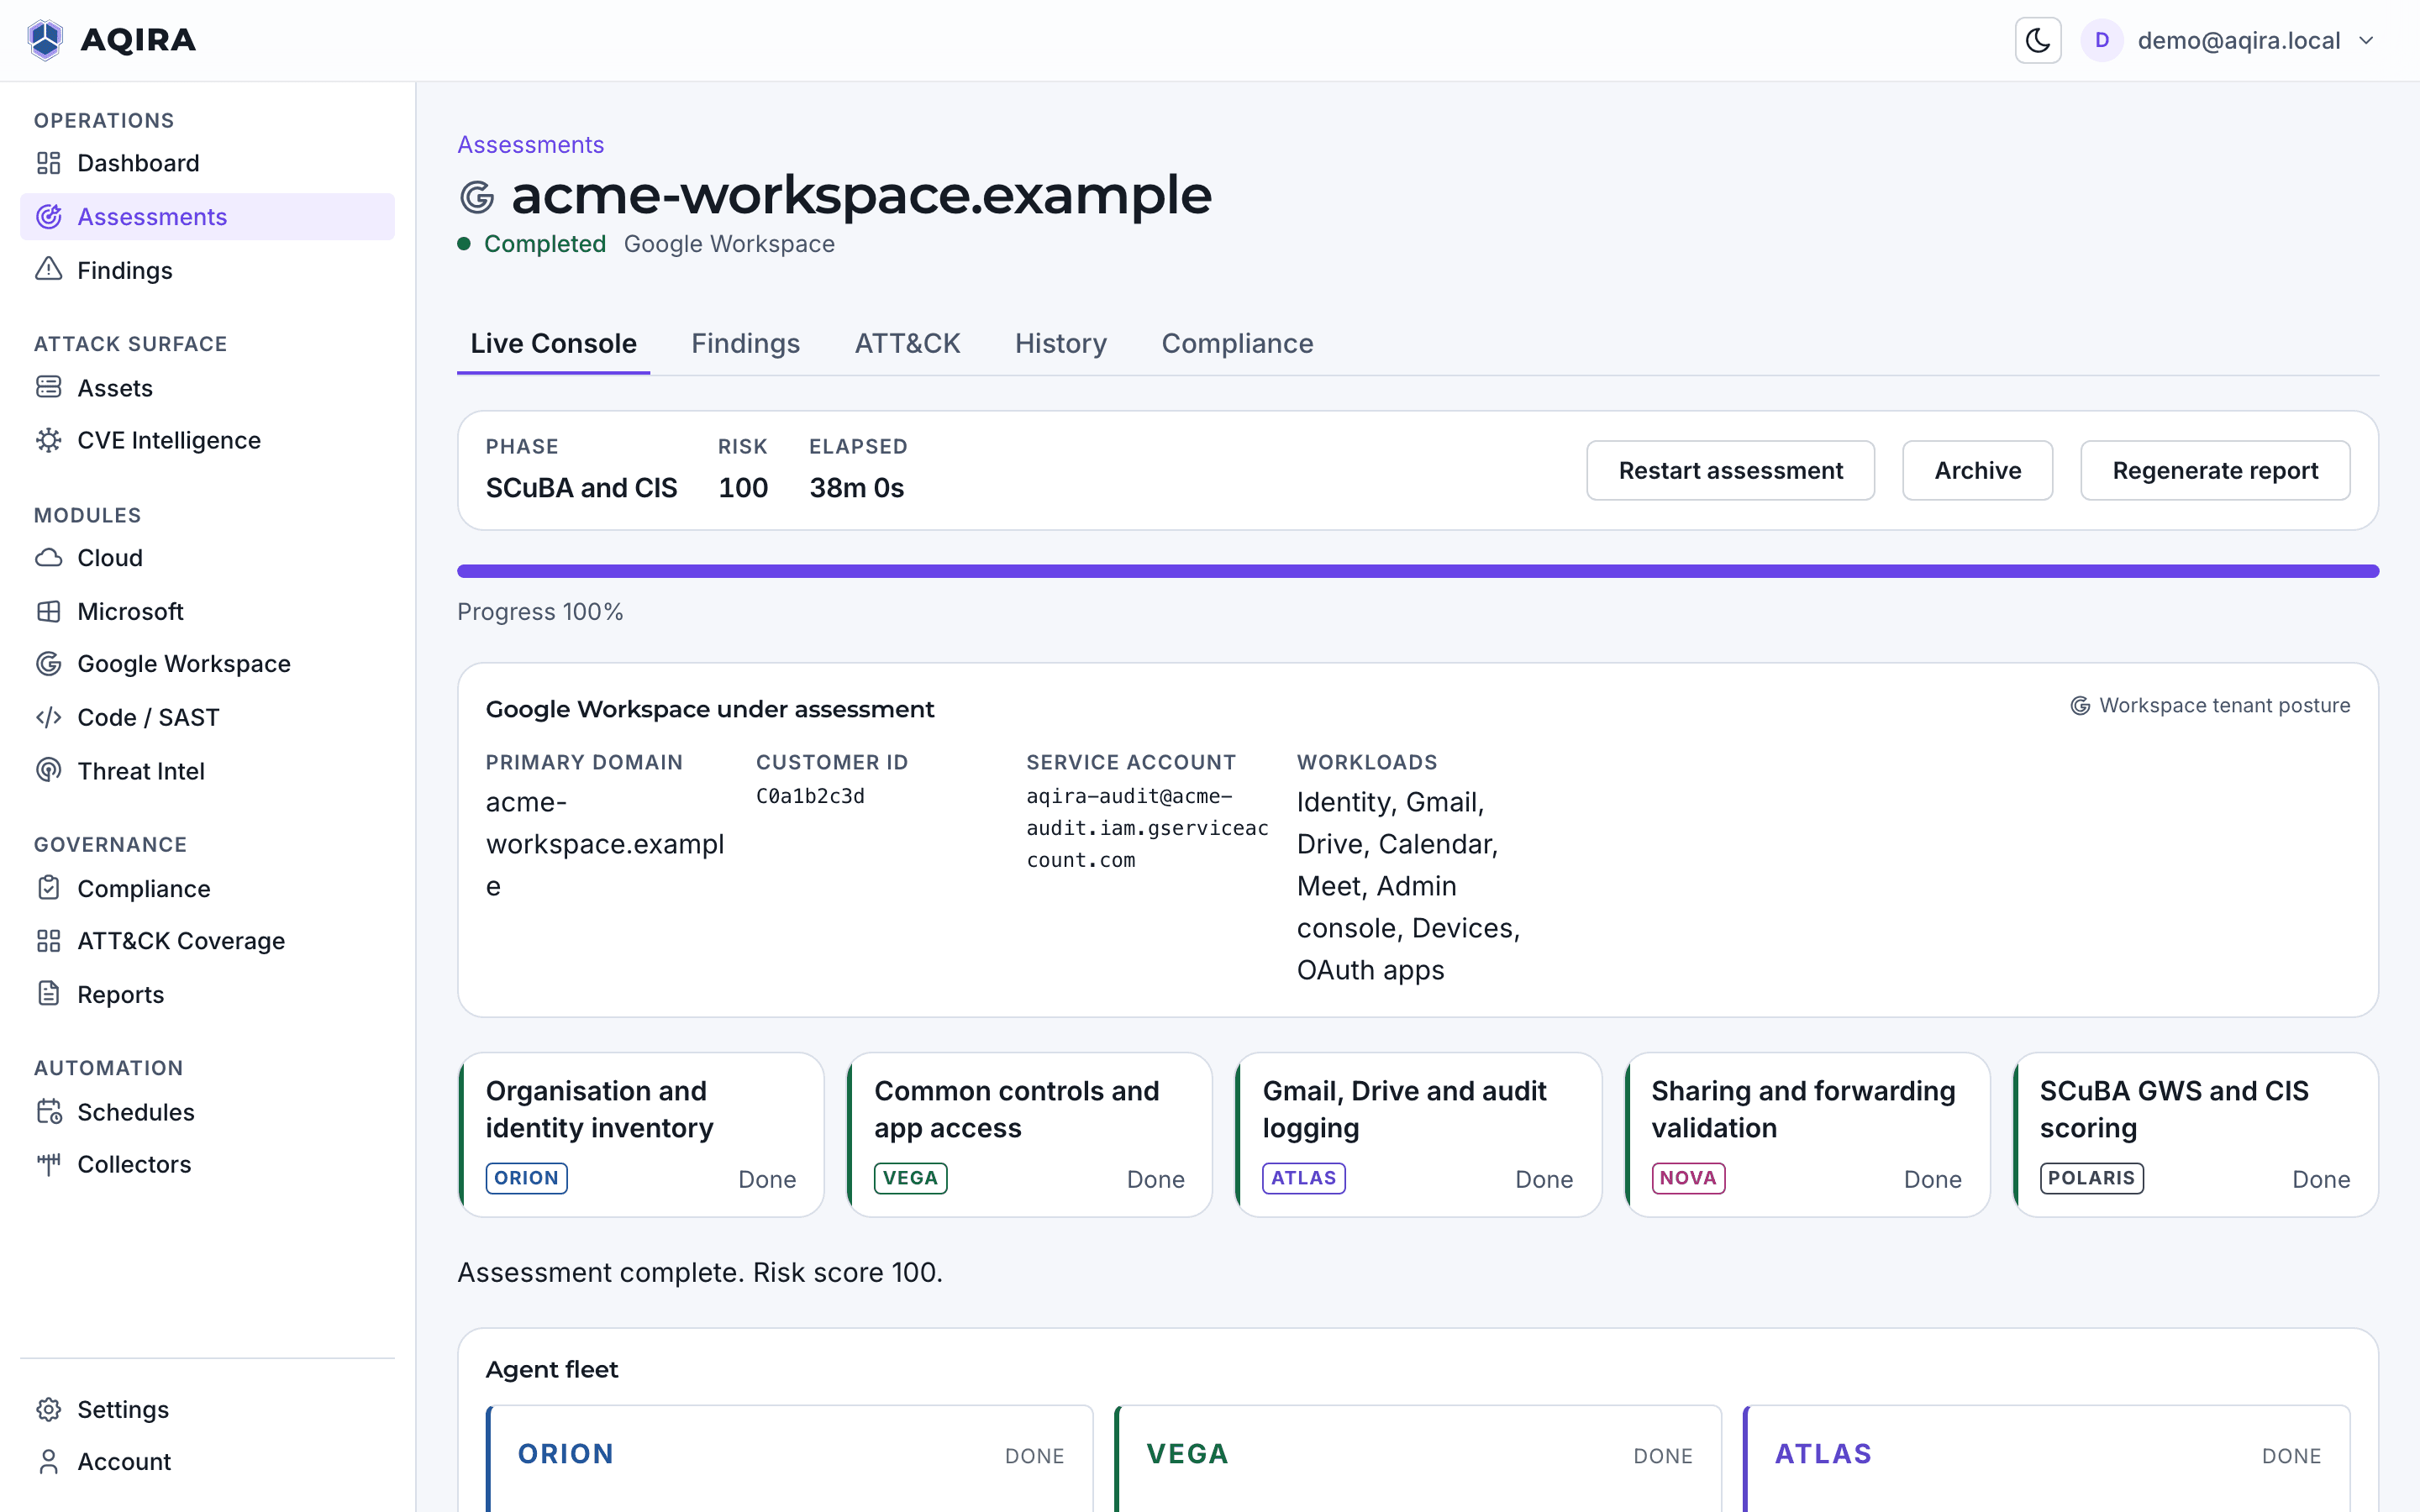
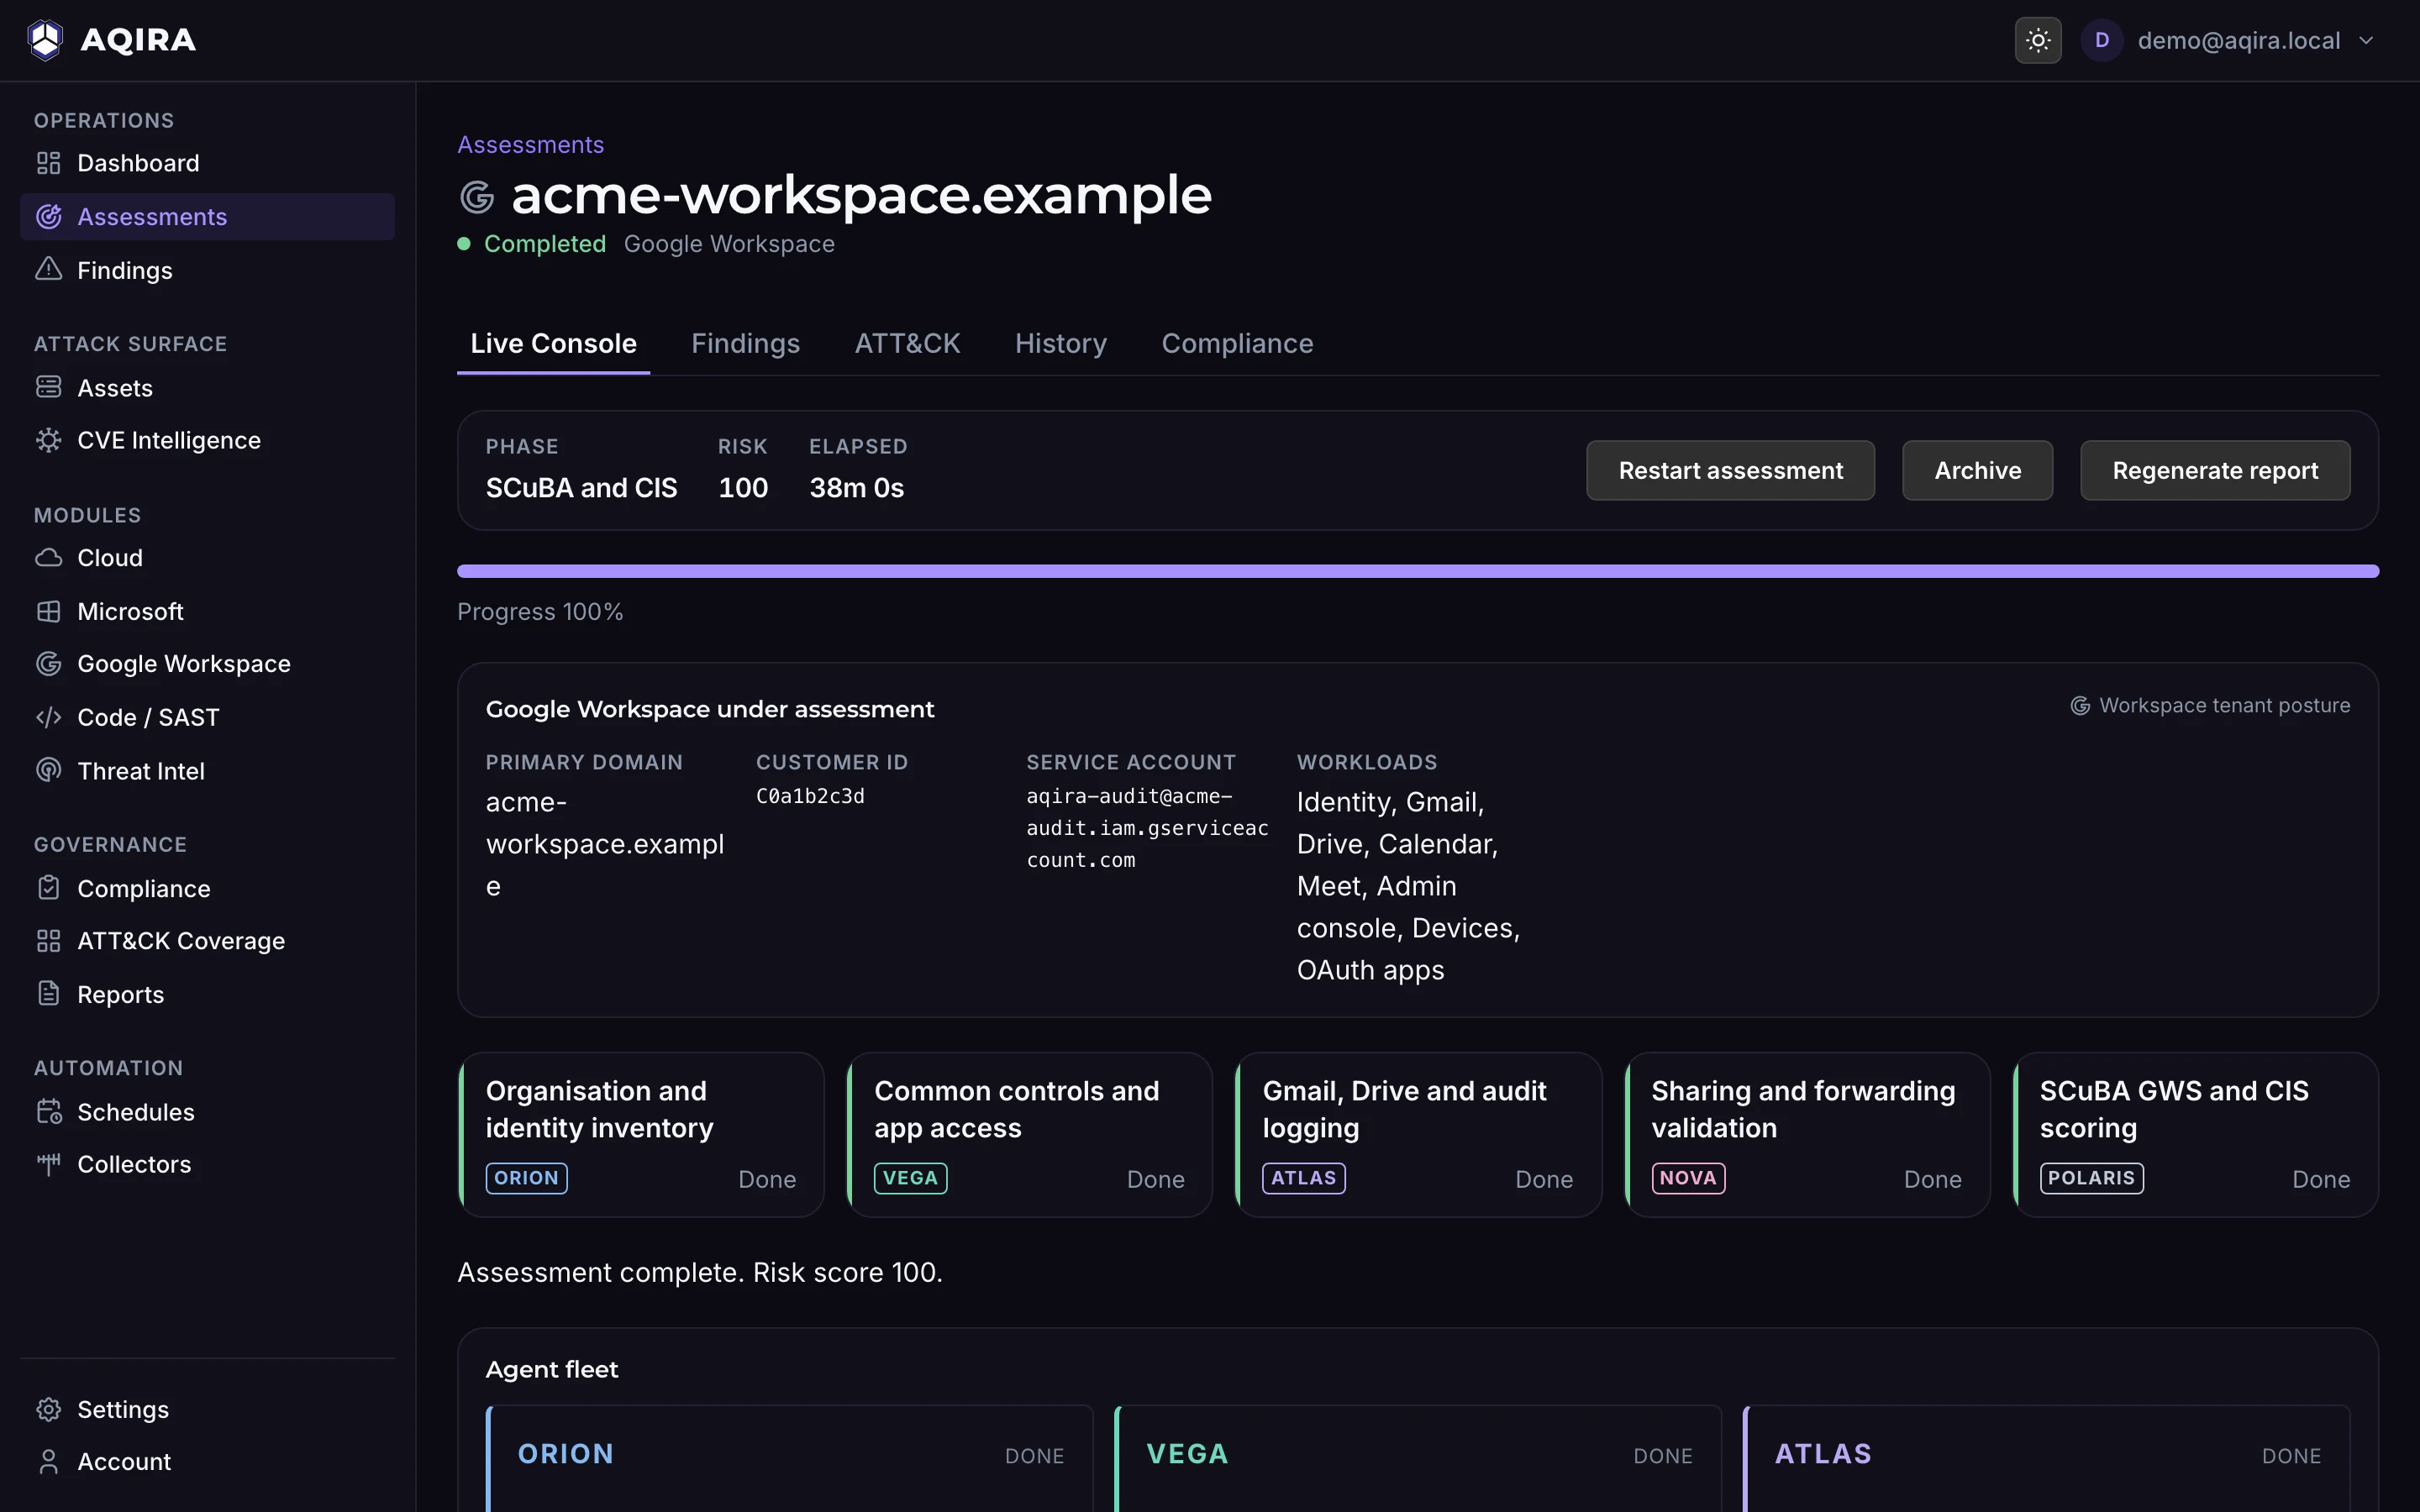
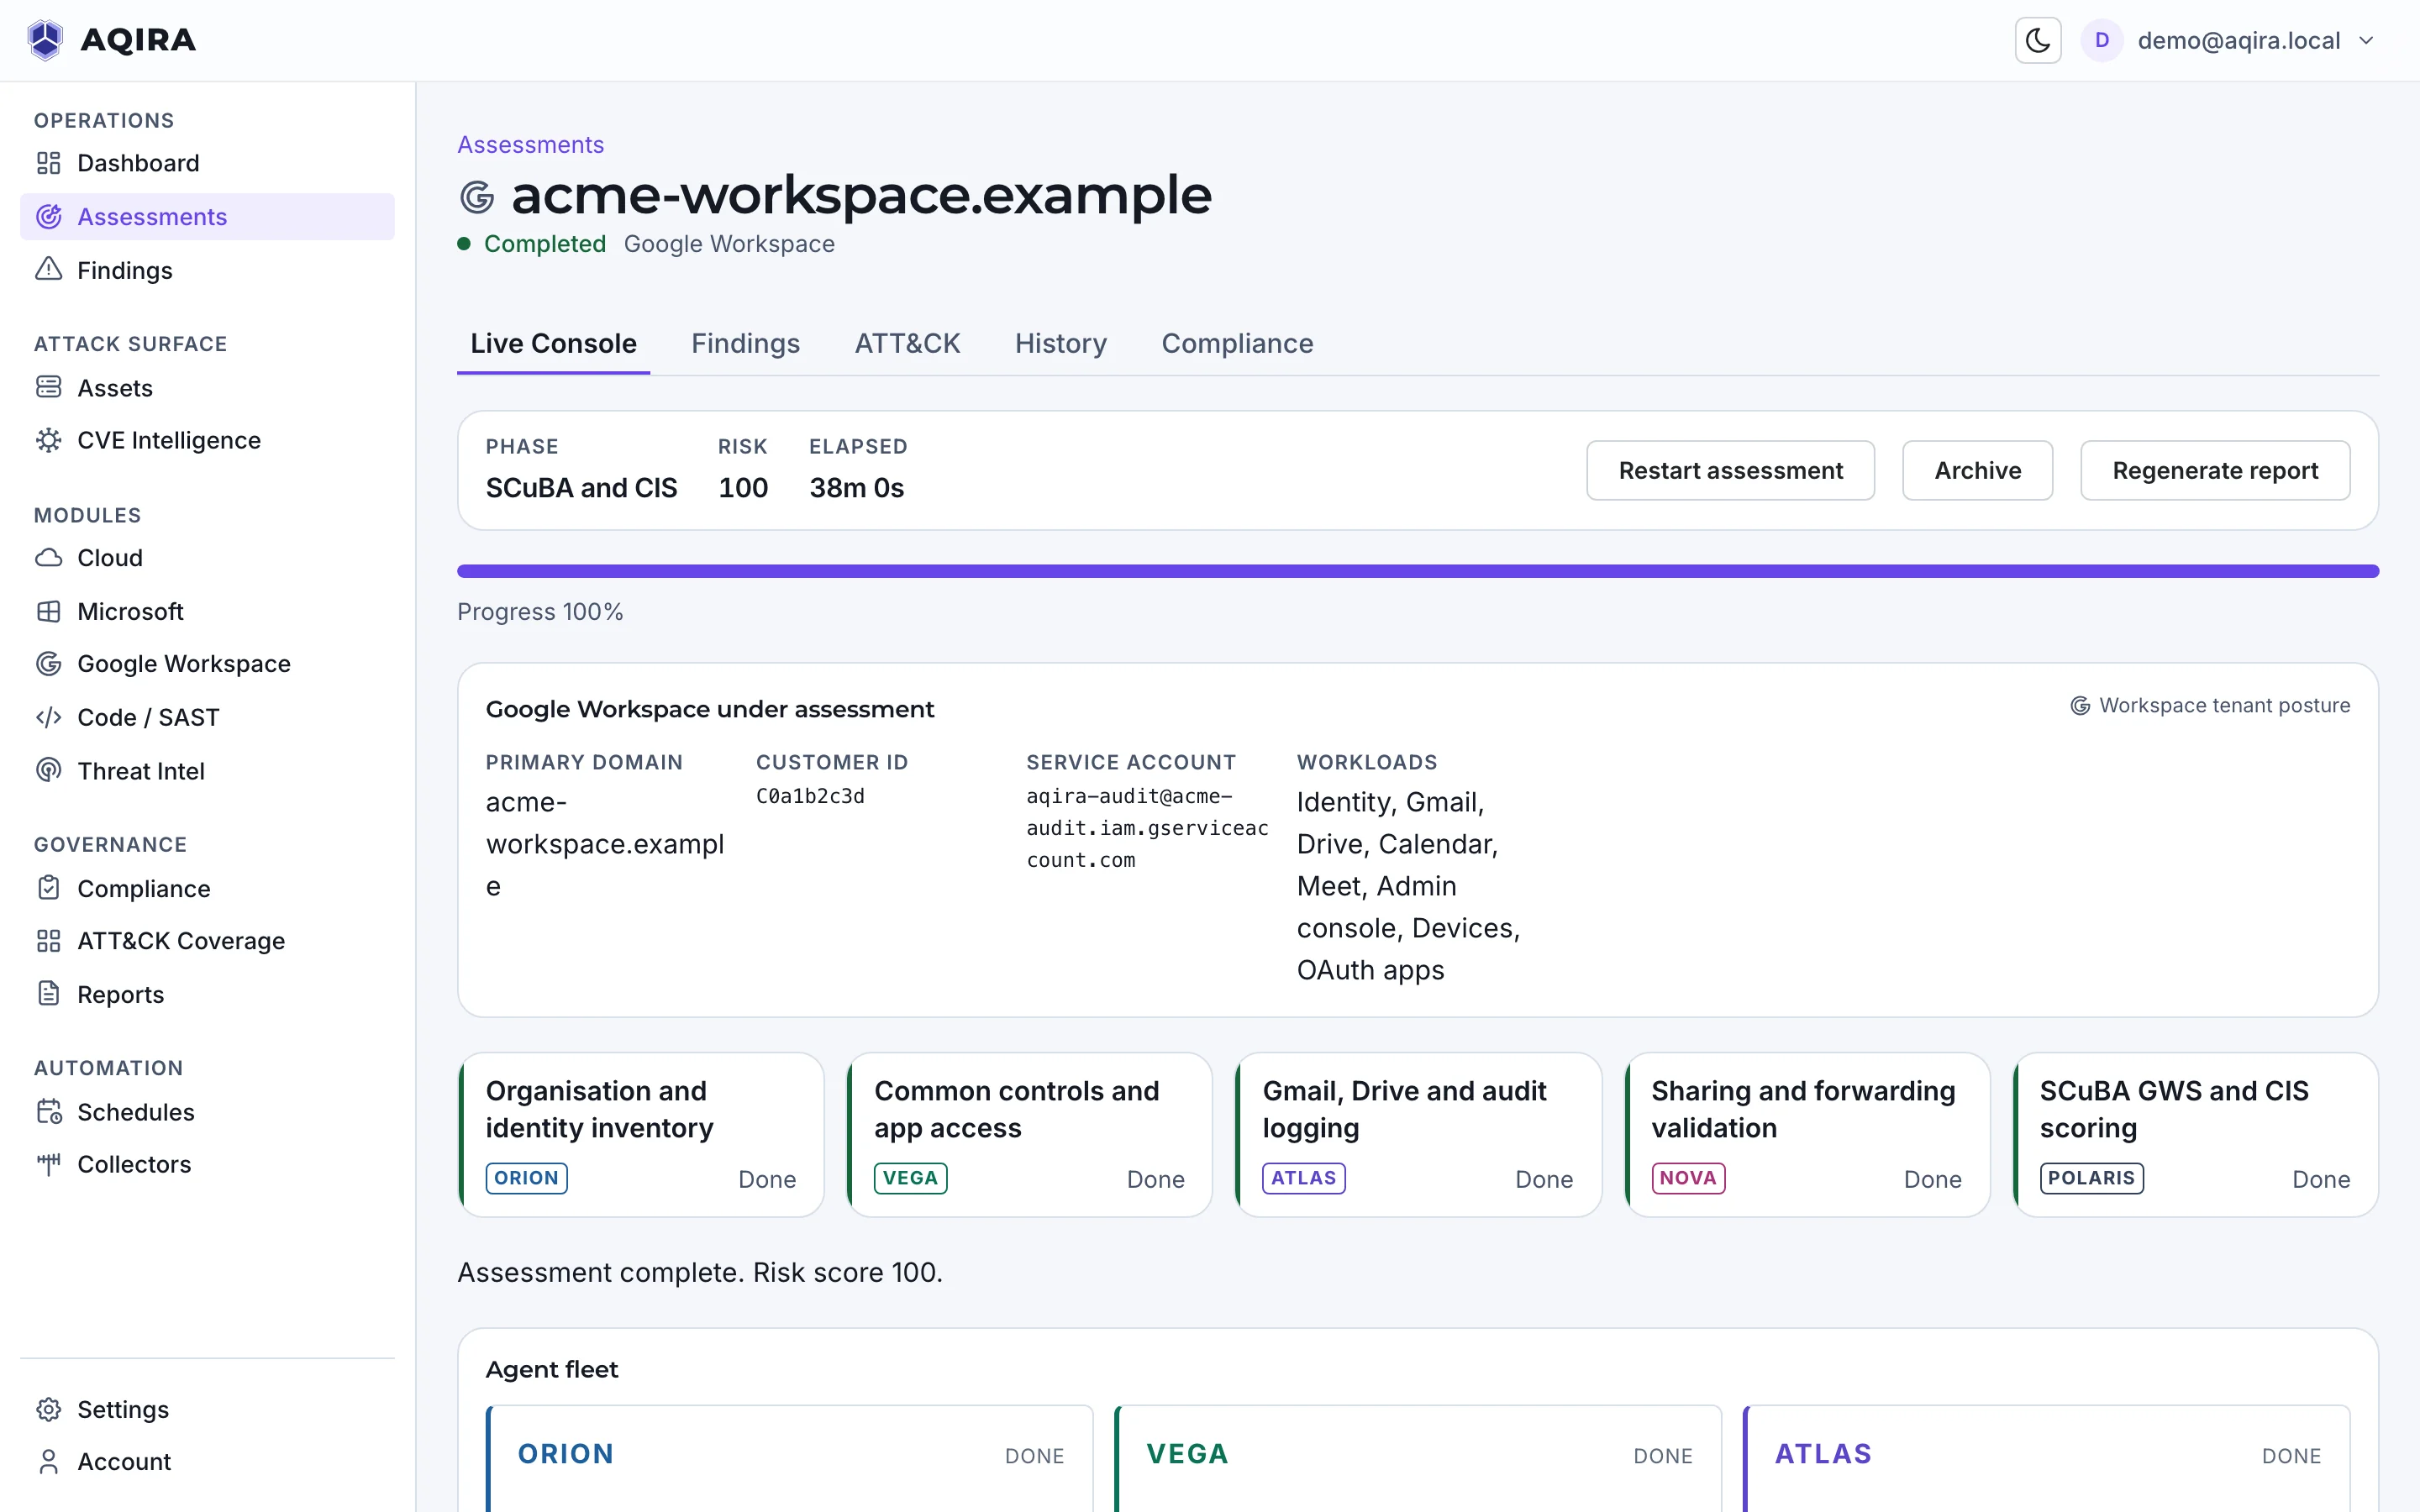
ORION, VEGA, ATLAS, NOVA, POLARIS, SCRIBE
What each agent does on this input
The same six agents, in the same order; on a Workspace tenant this is the work.
01ORIONOrganisation and identity inventory
Inventories the tenant's principals, roles and applications.
- Tenant inventory
- Identity graphing
- Open-source intel
02VEGACommon controls and app access
Reads identity and collaboration workload policy.
- Policy readout
- Identity posture
- Integration scanning
03ATLASGmail, Drive and audit logging
Reviews mail flow, endpoint posture and audit logging.
- Mail-flow review
- Endpoint posture
- Audit review
04NOVASharing and forwarding validation
Validates identity attack paths to benign proof.
- Attack-path validation
- Breach exposure
- Vulnerability correlation
05POLARISSCuBA GWS and CIS scoring
Consolidates what the others found. Scores the tenant against CIS Google Workspace and CISA SCuBA.
06SCRIBEReport
Writes the client-deliverable report from the same evidence the console shows.
The findings it raises
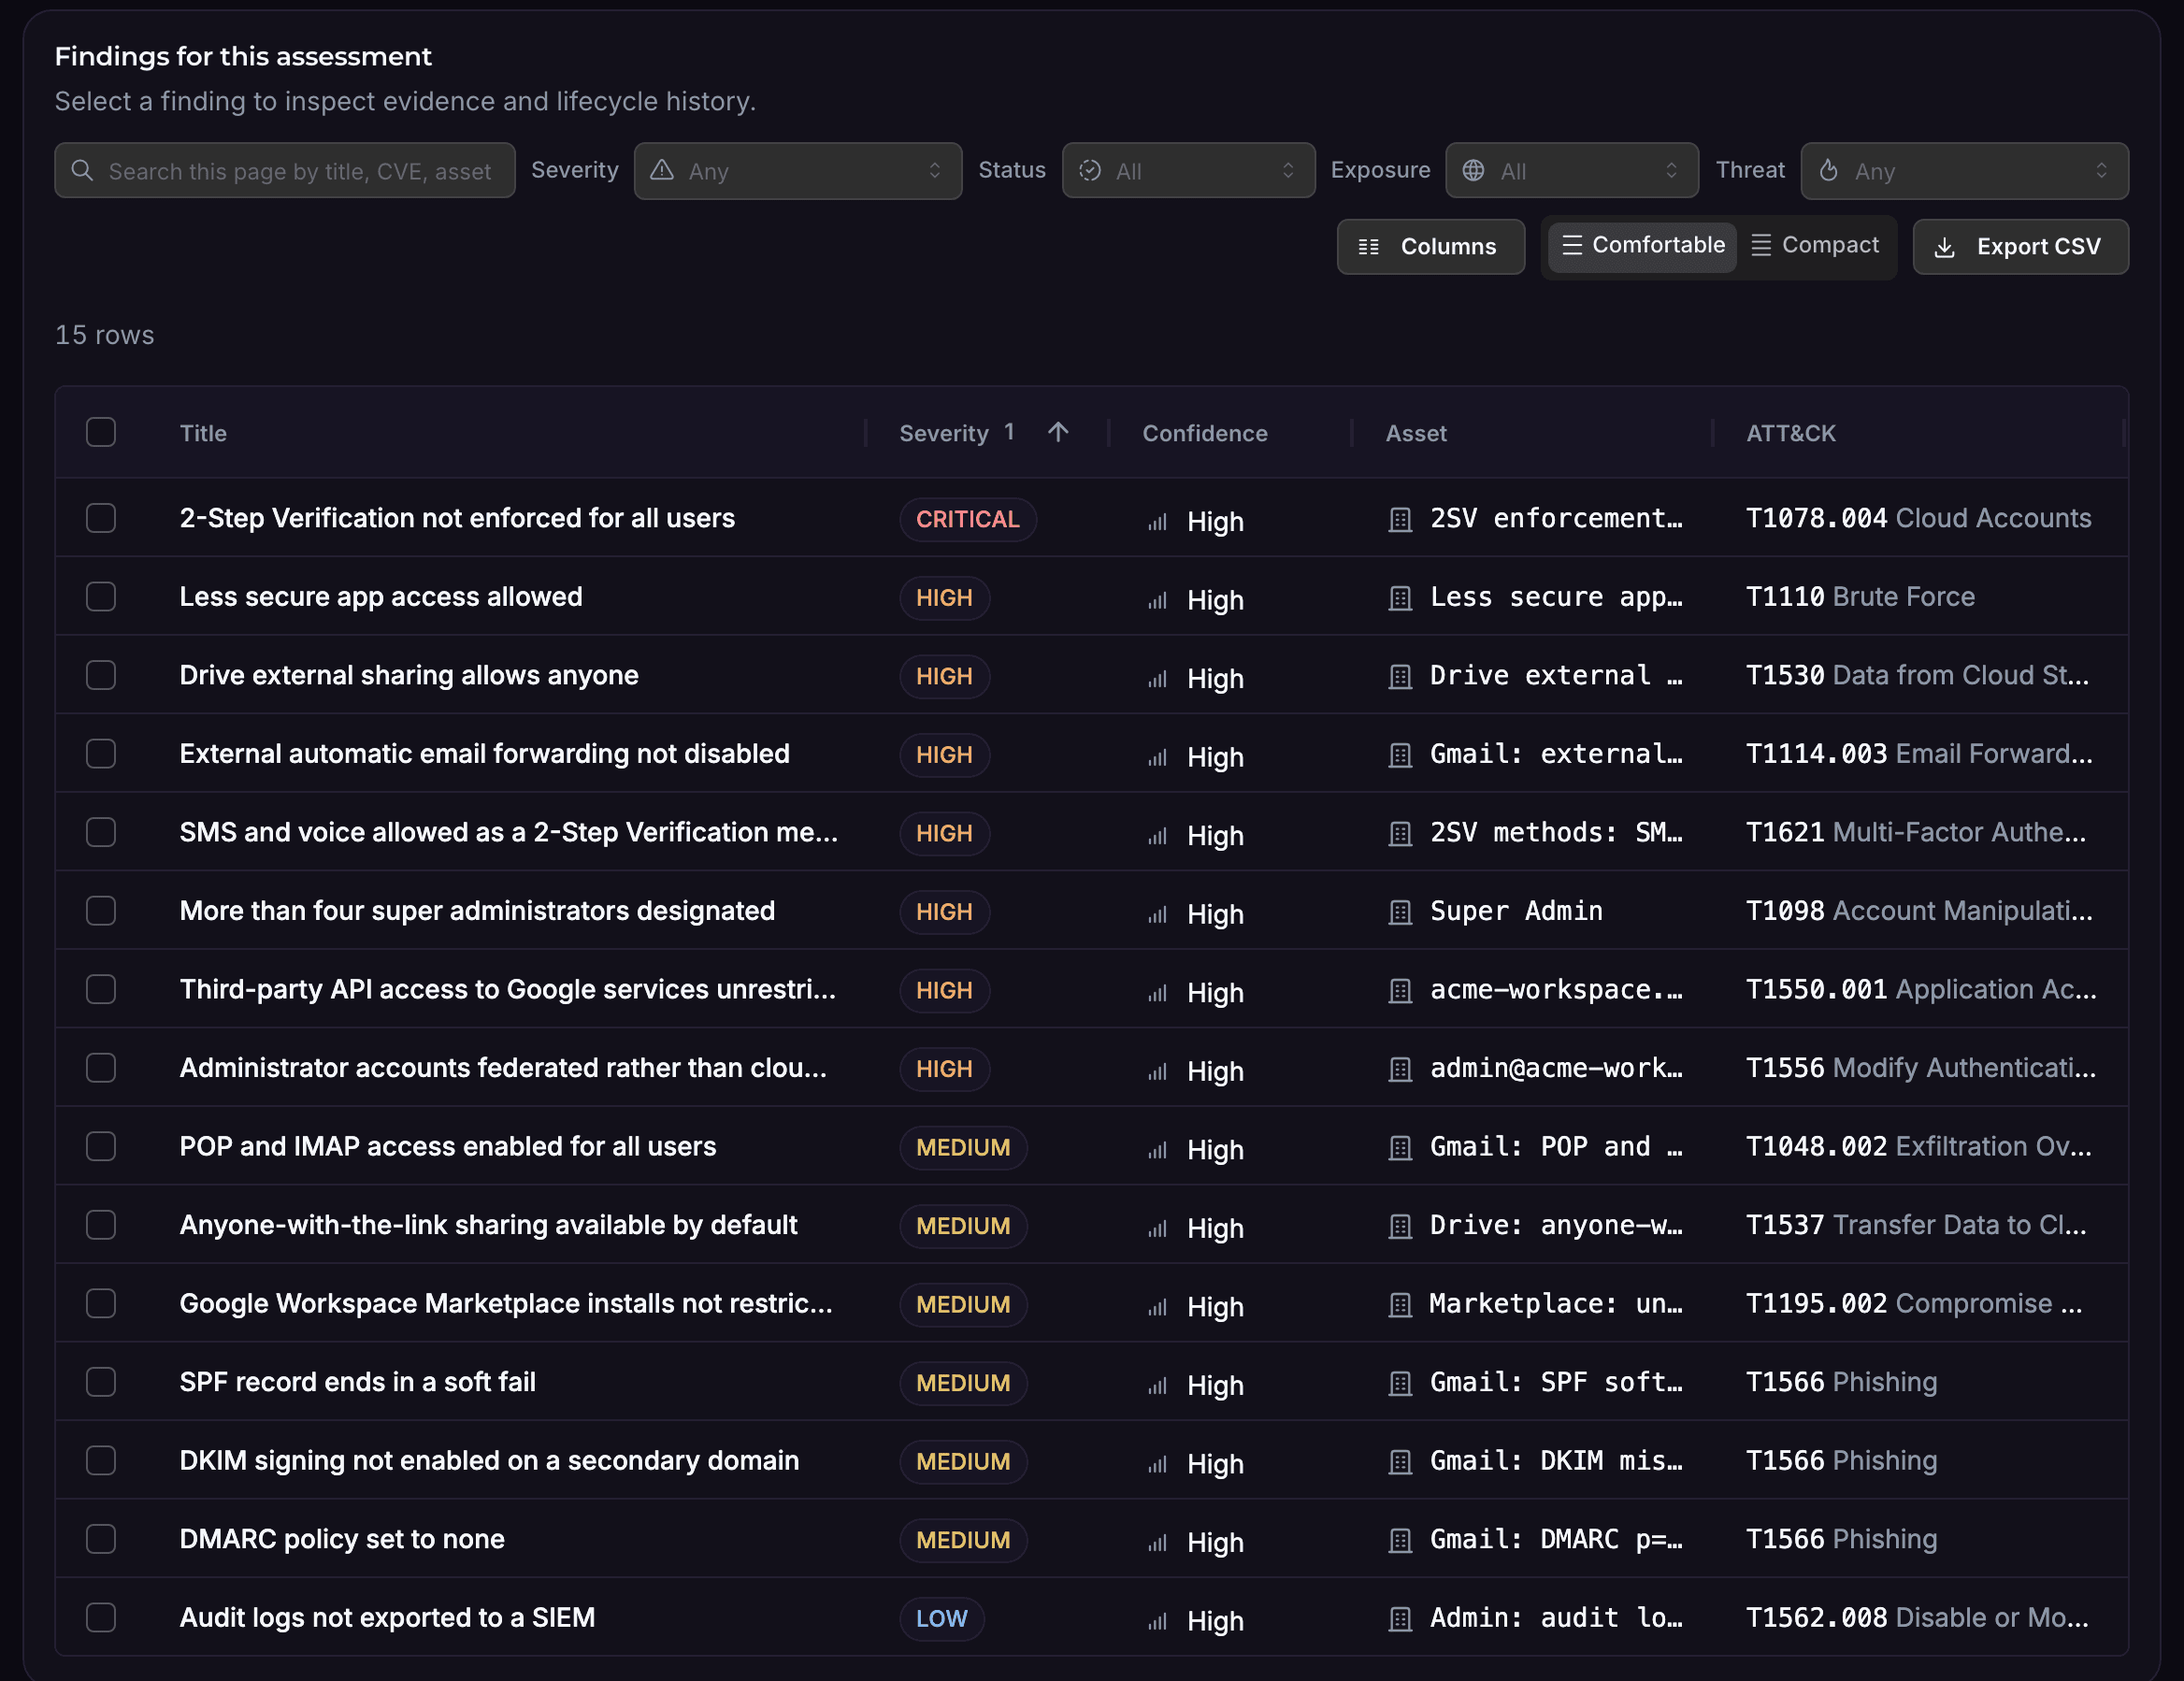
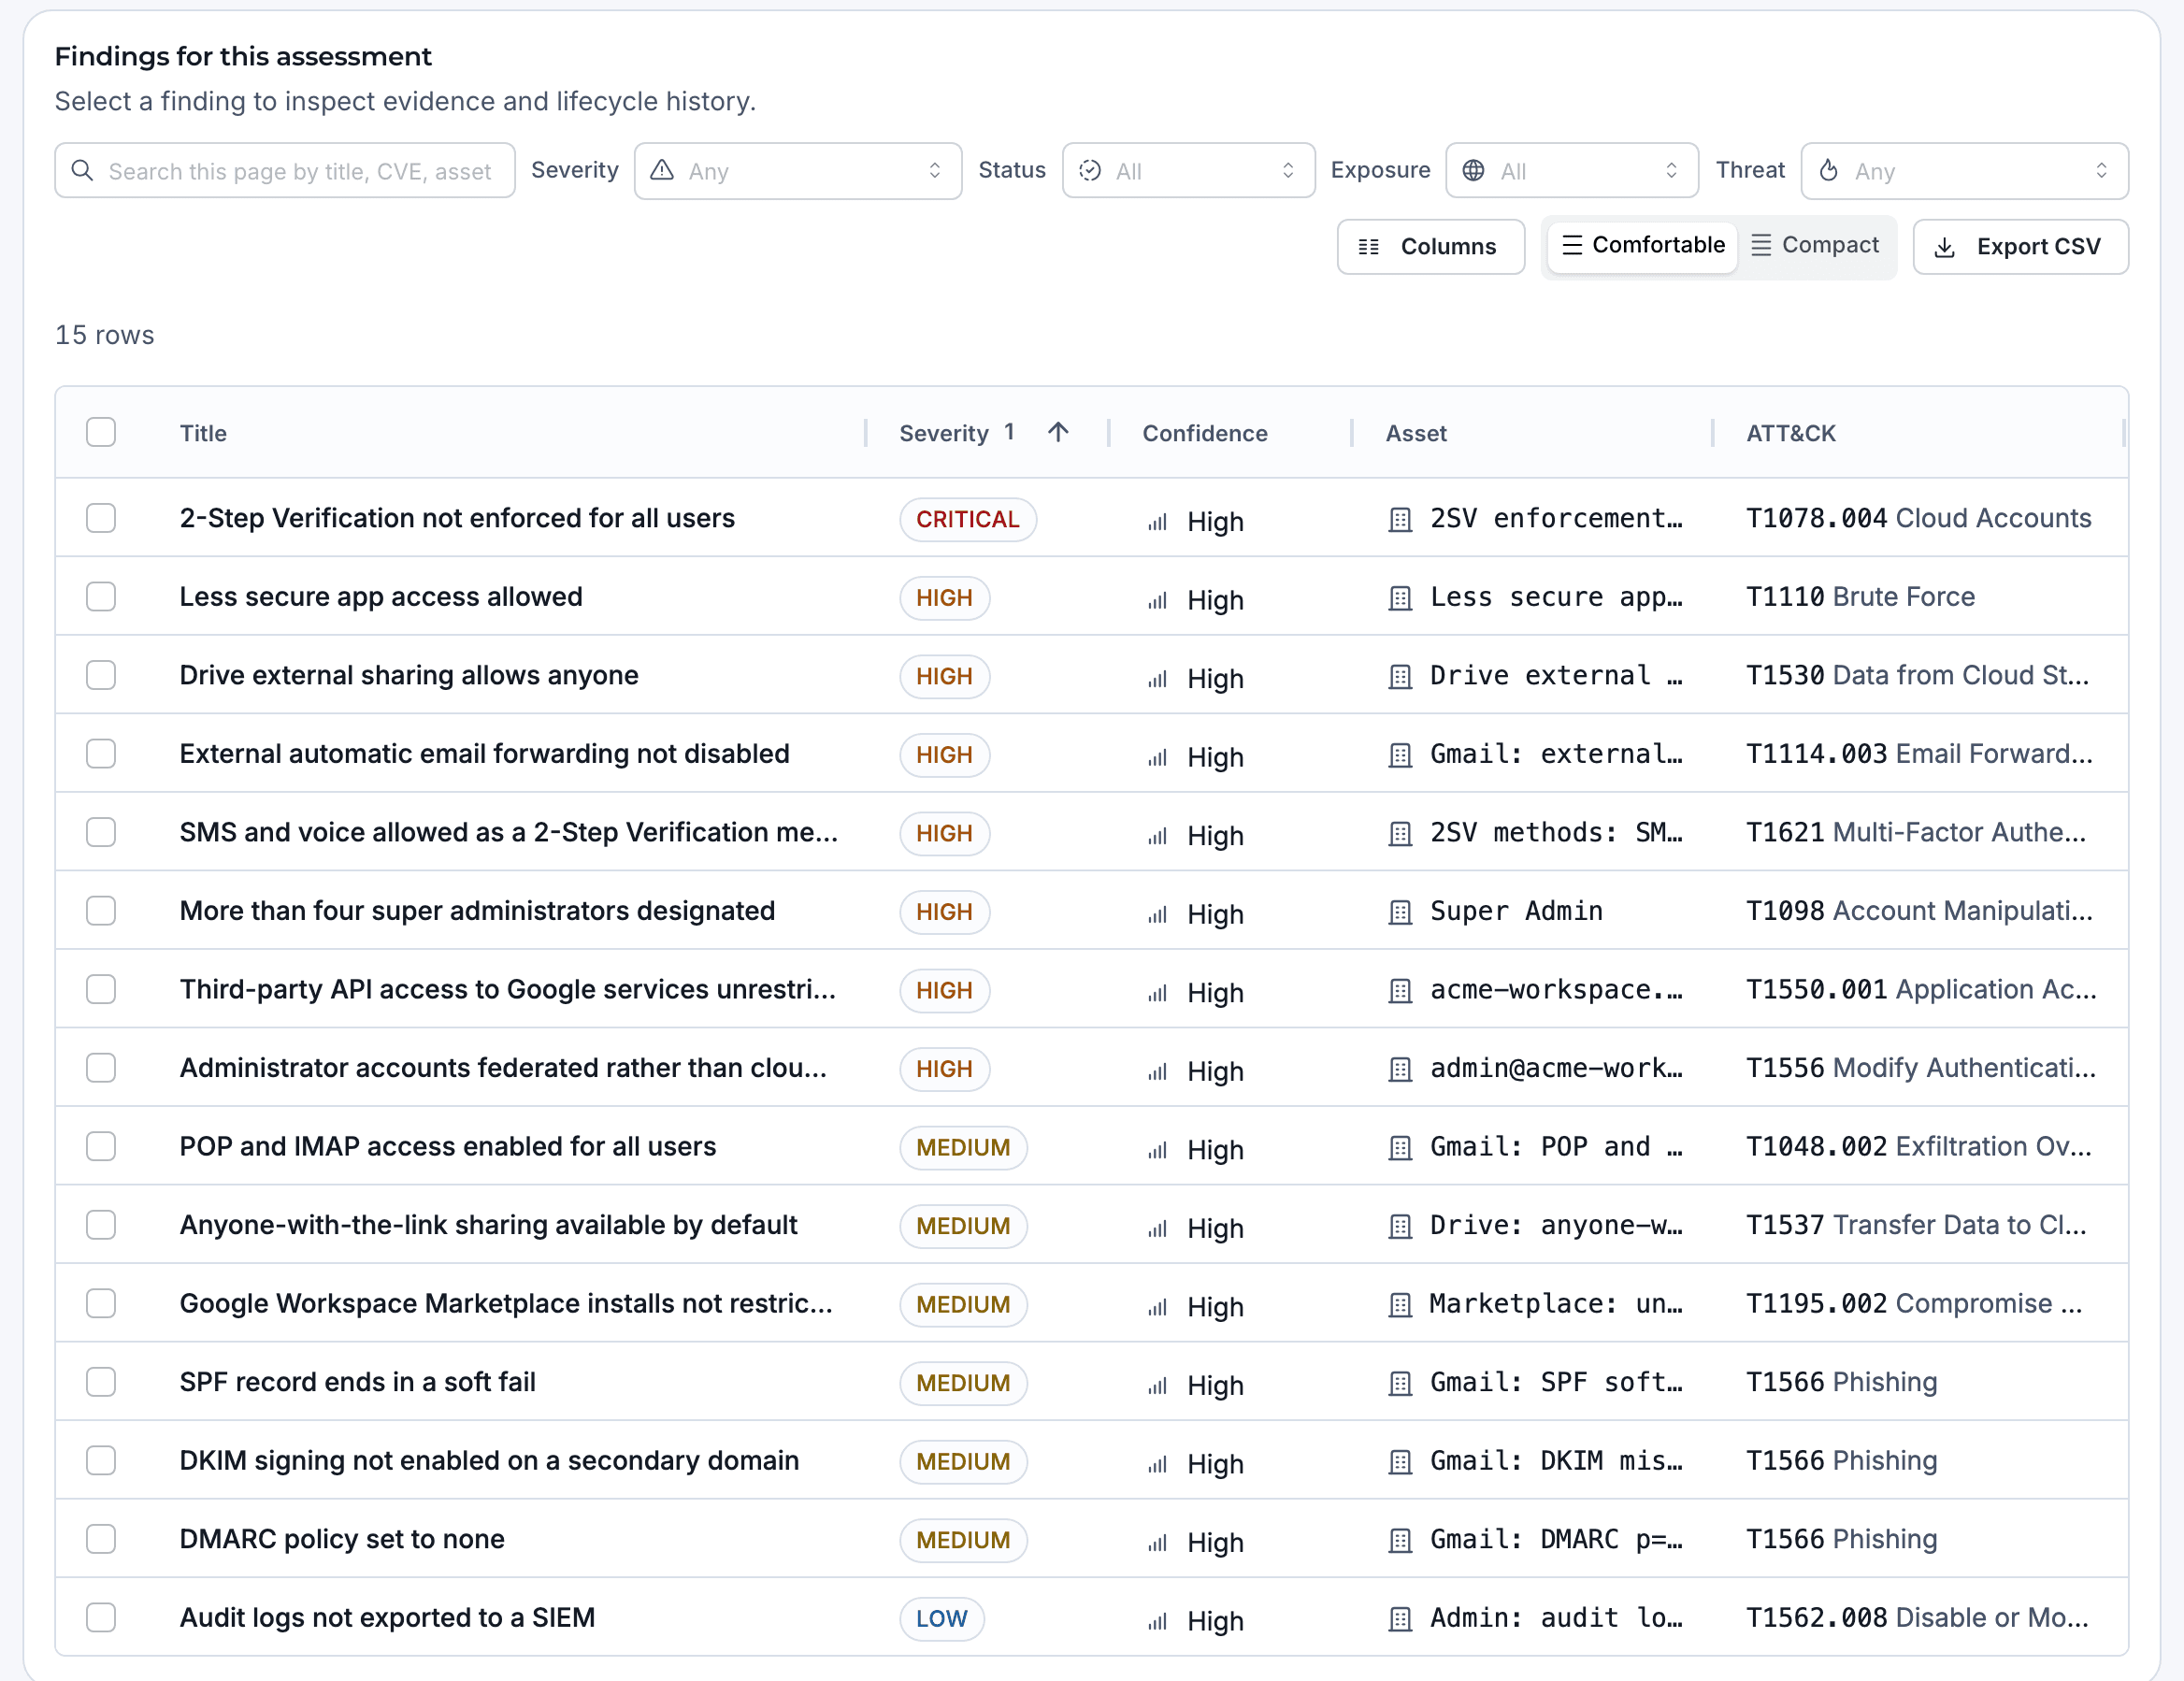
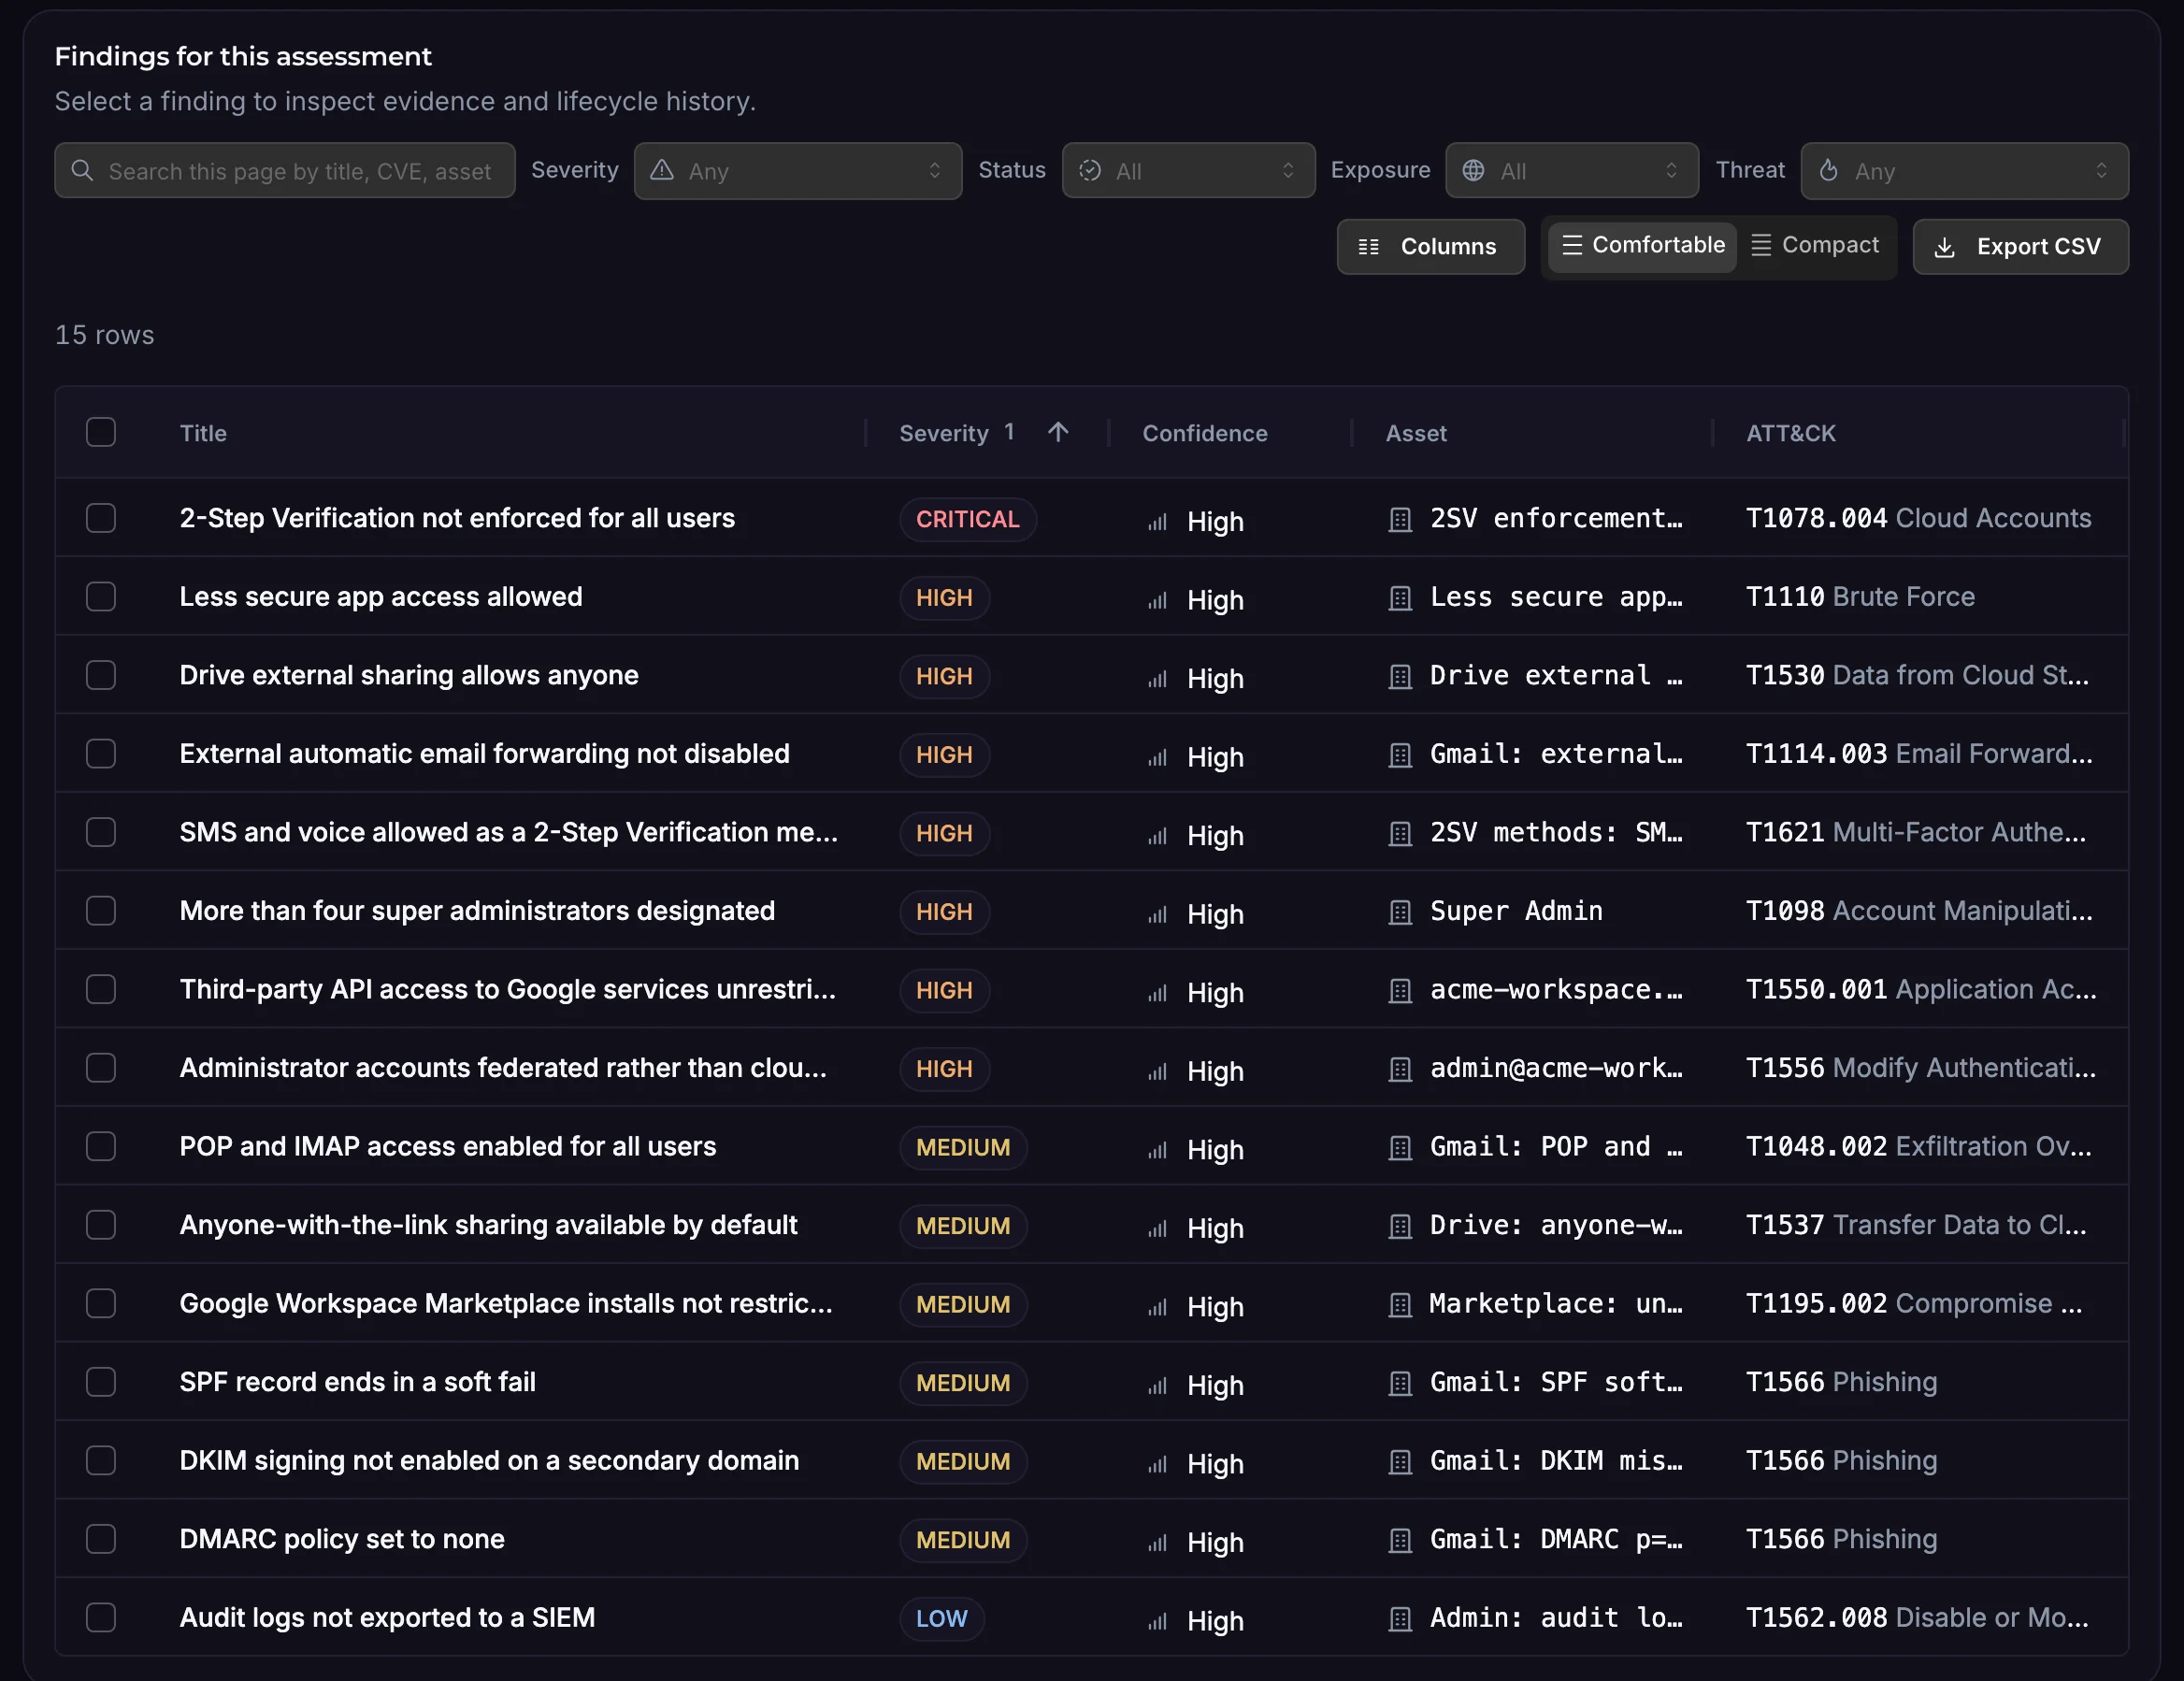
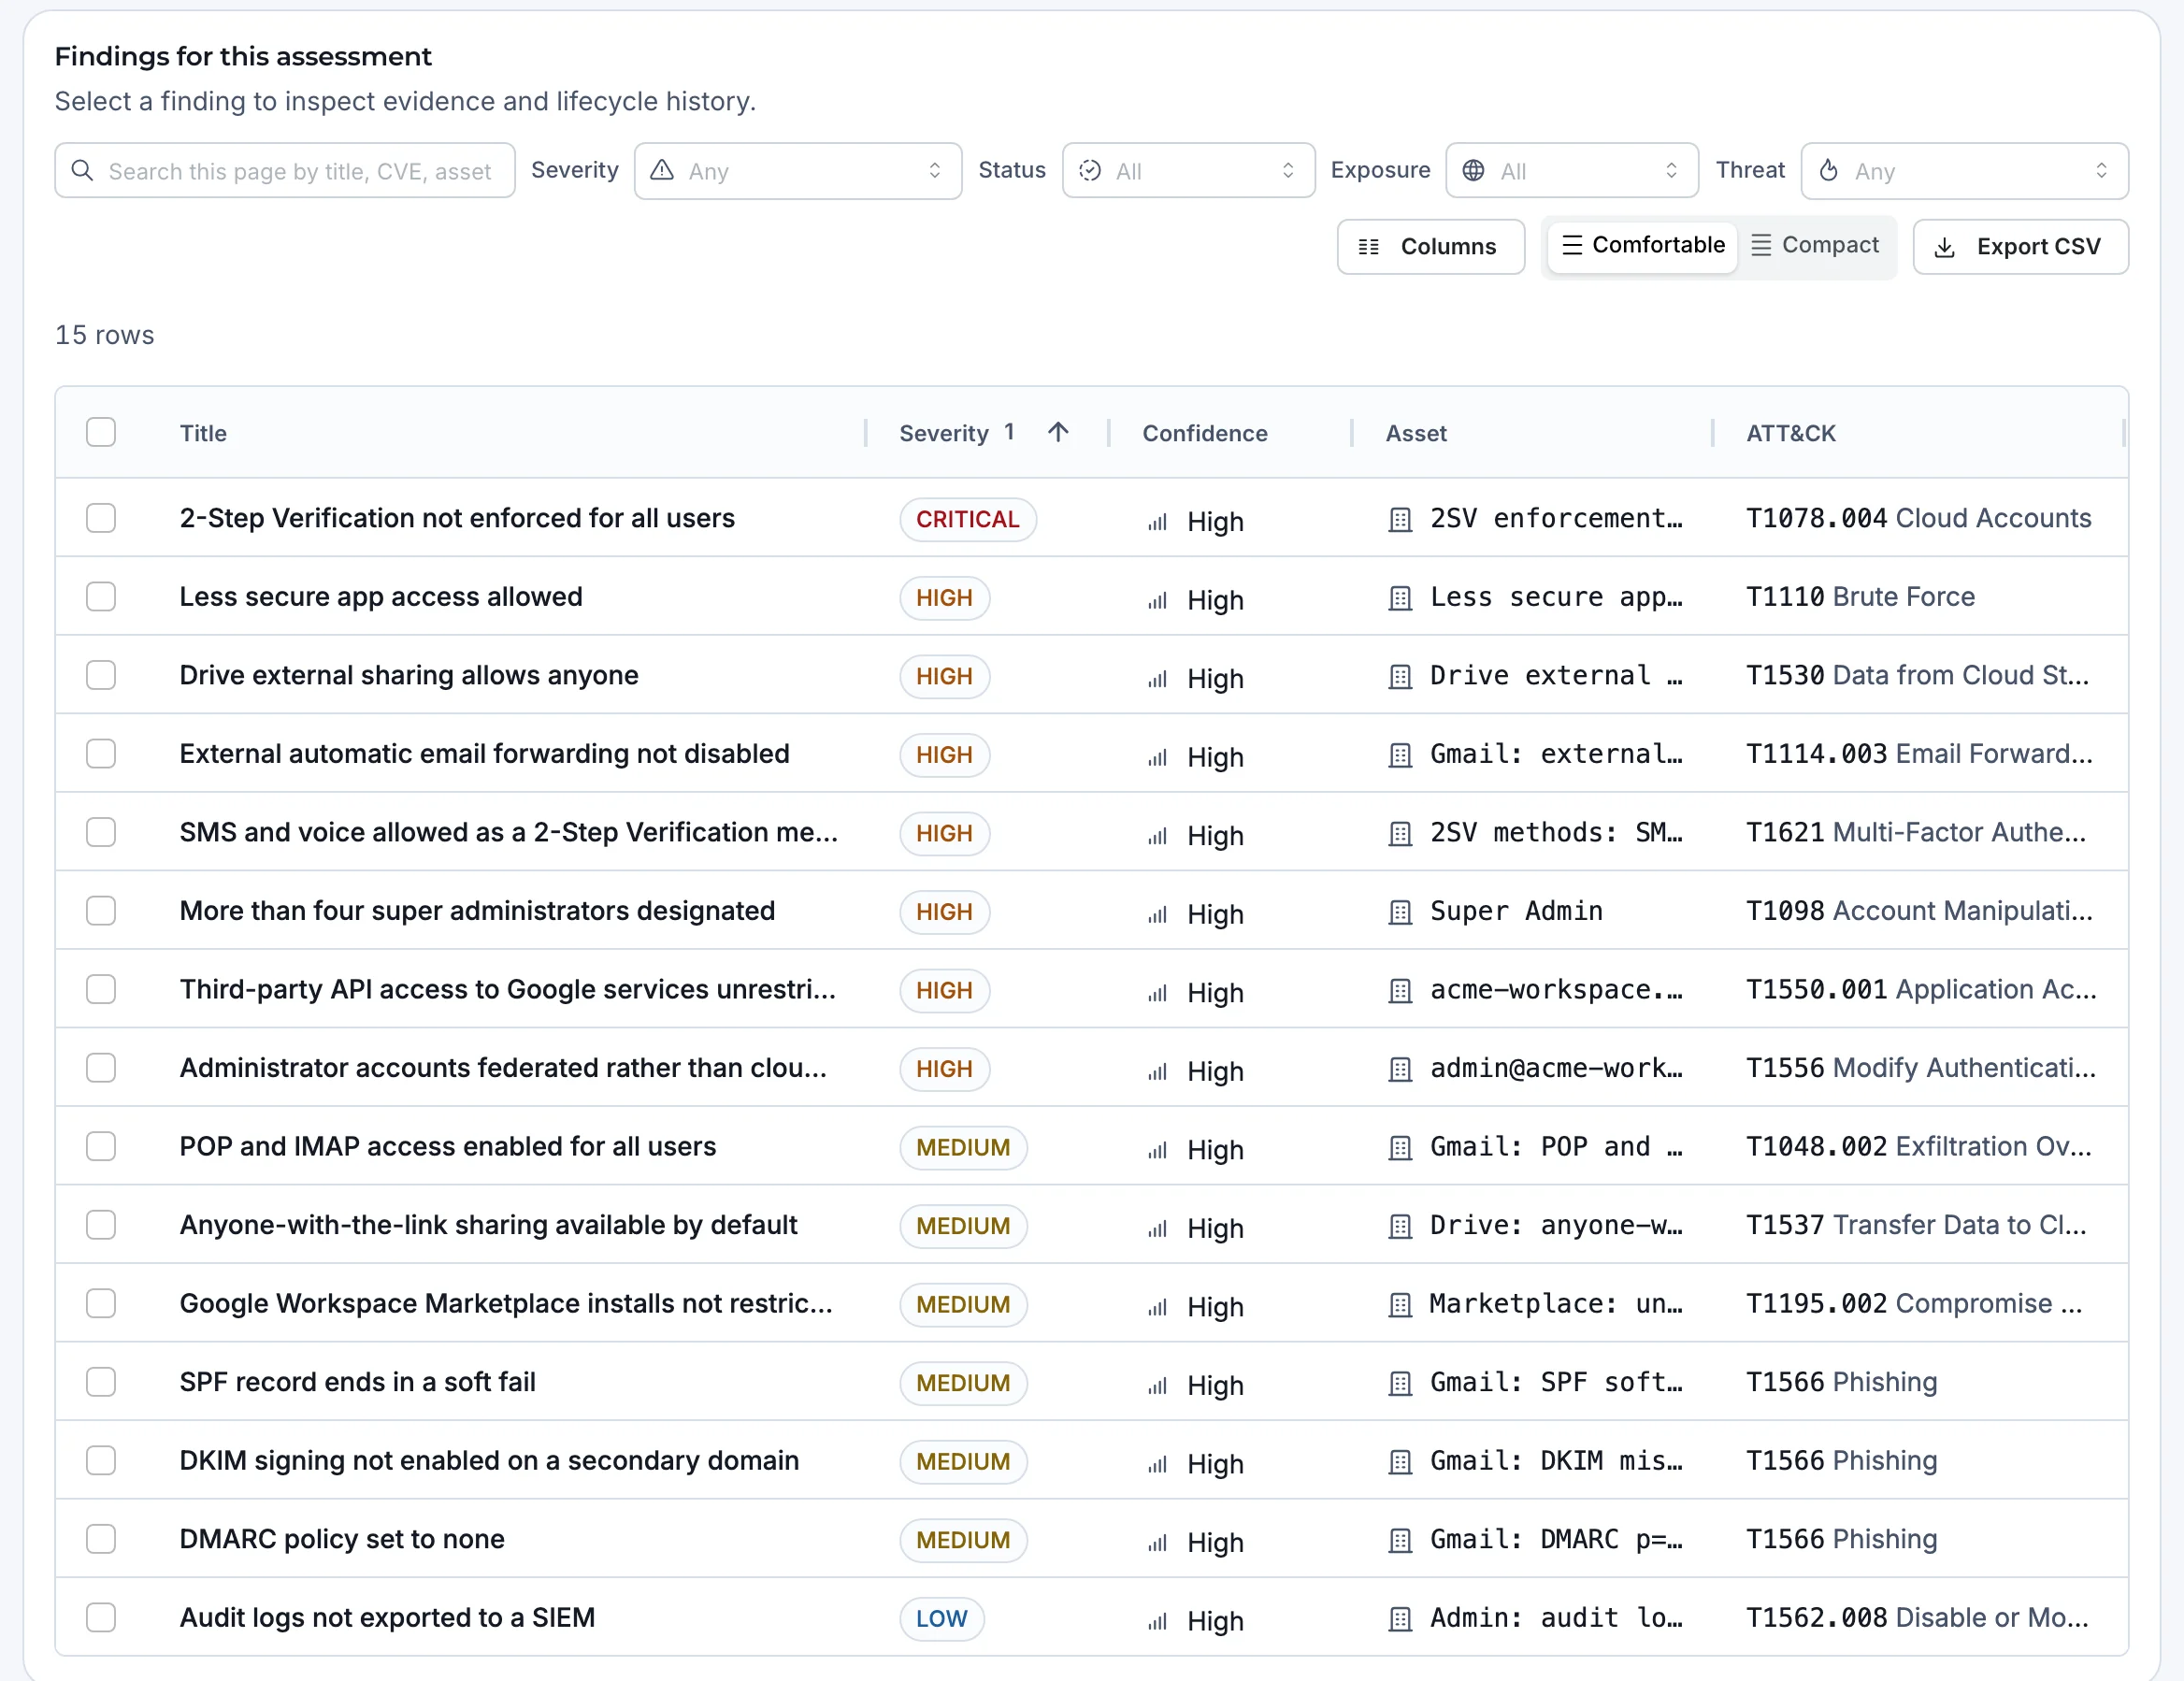
Examples of what AQIRA reports on a Workspace tenant, each with evidence, steps to reproduce, remediation in priority order and its ATT&CK technique.
- 2-Step Verification not enforced for all users
- SMS and voice allowed as 2-Step Verification methods
- More than four super administrators
- Third-party API access to Google services unrestricted
- Less secure app access allowed
- External automatic email forwarding not disabled
- Drive external sharing that allows anyone
- Audit logs not exported to a SIEM
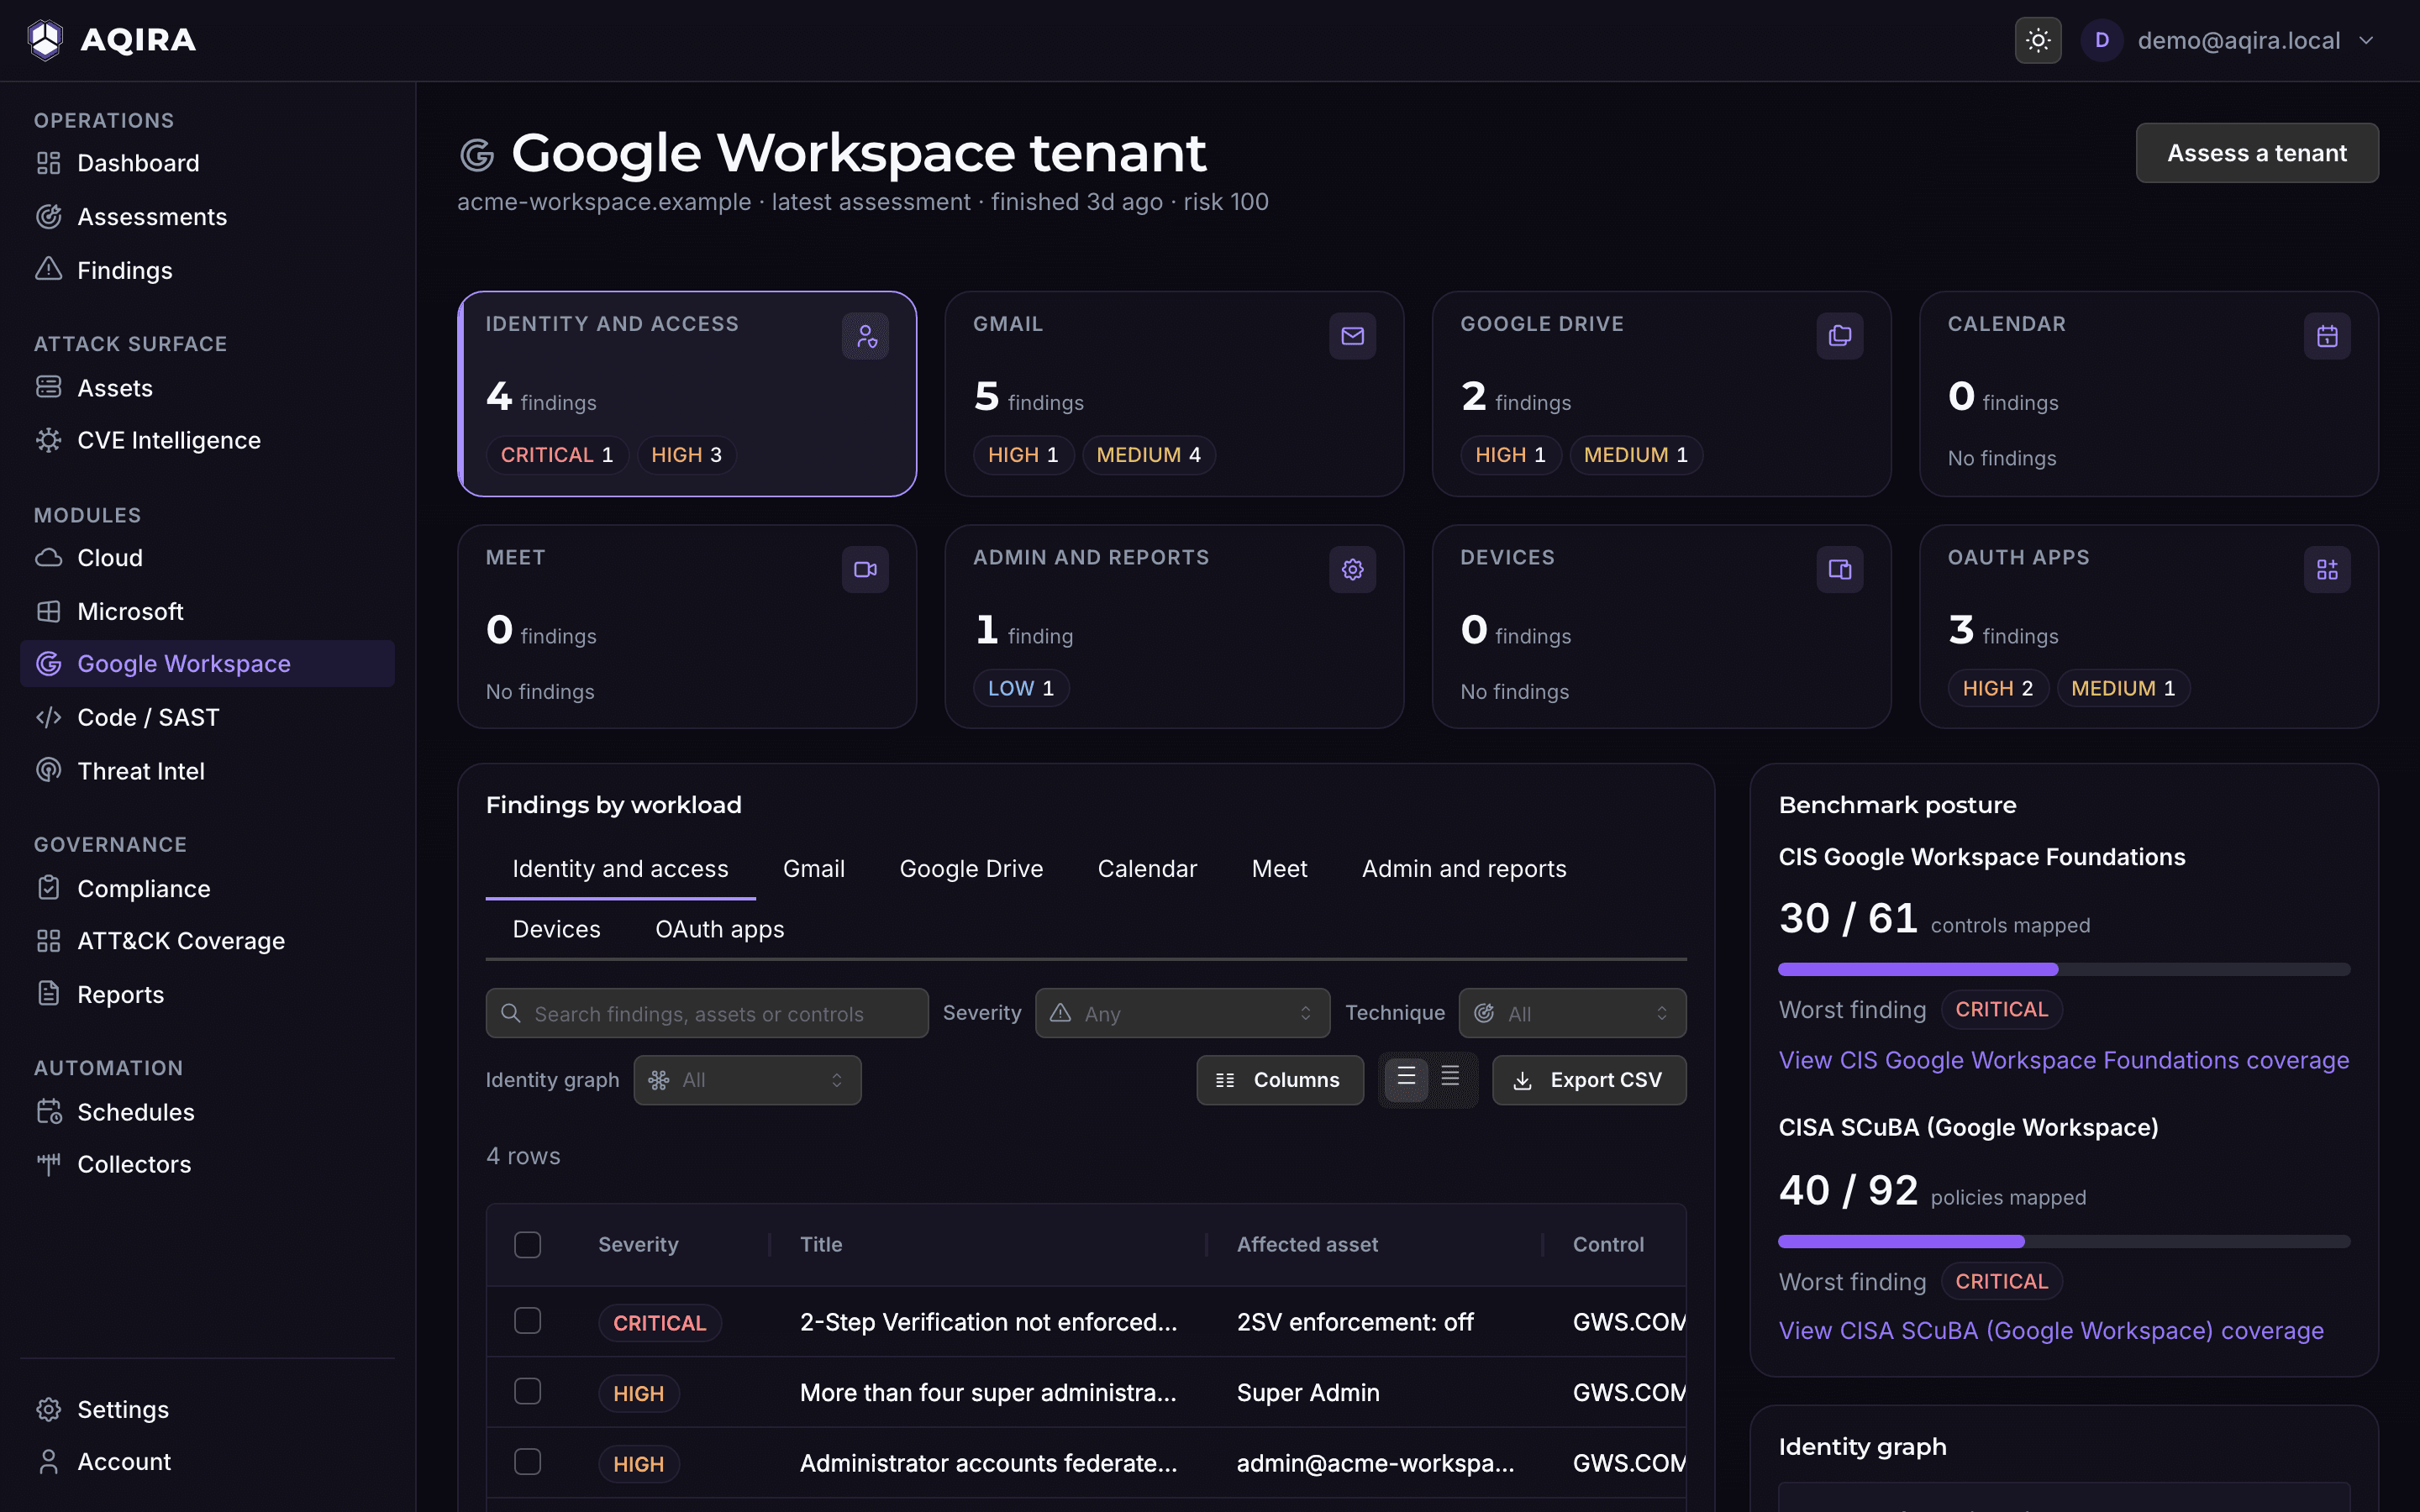
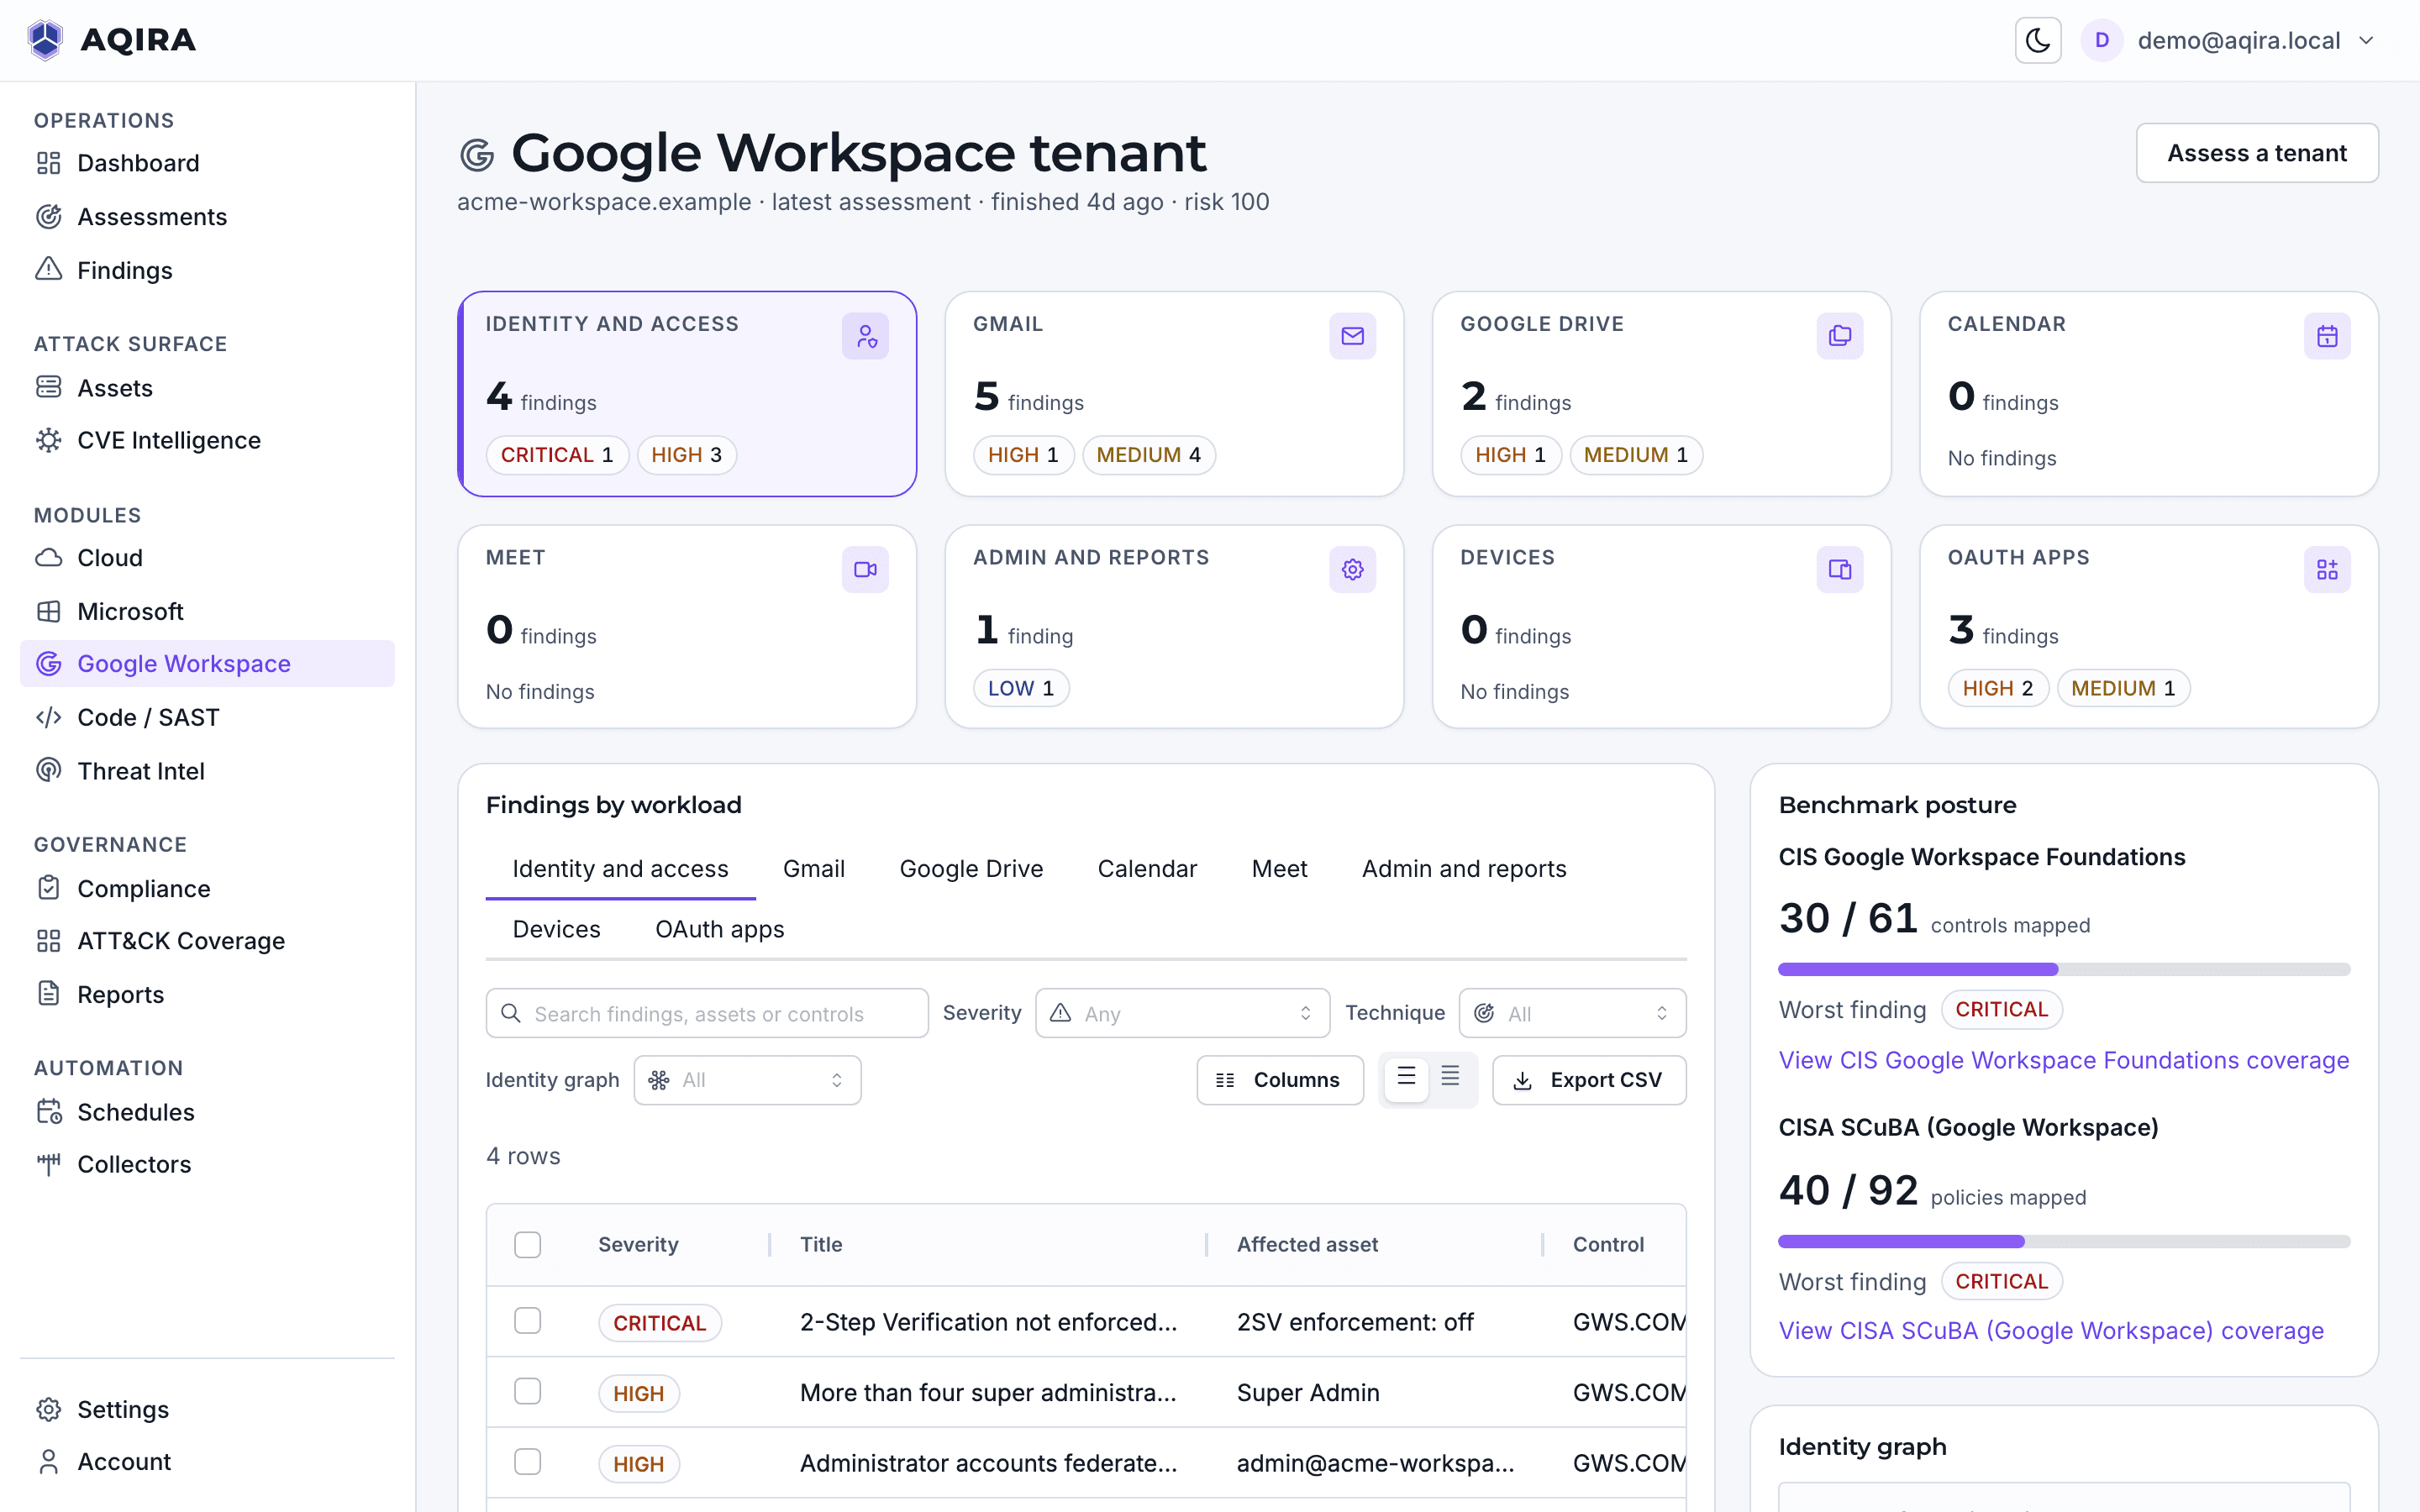
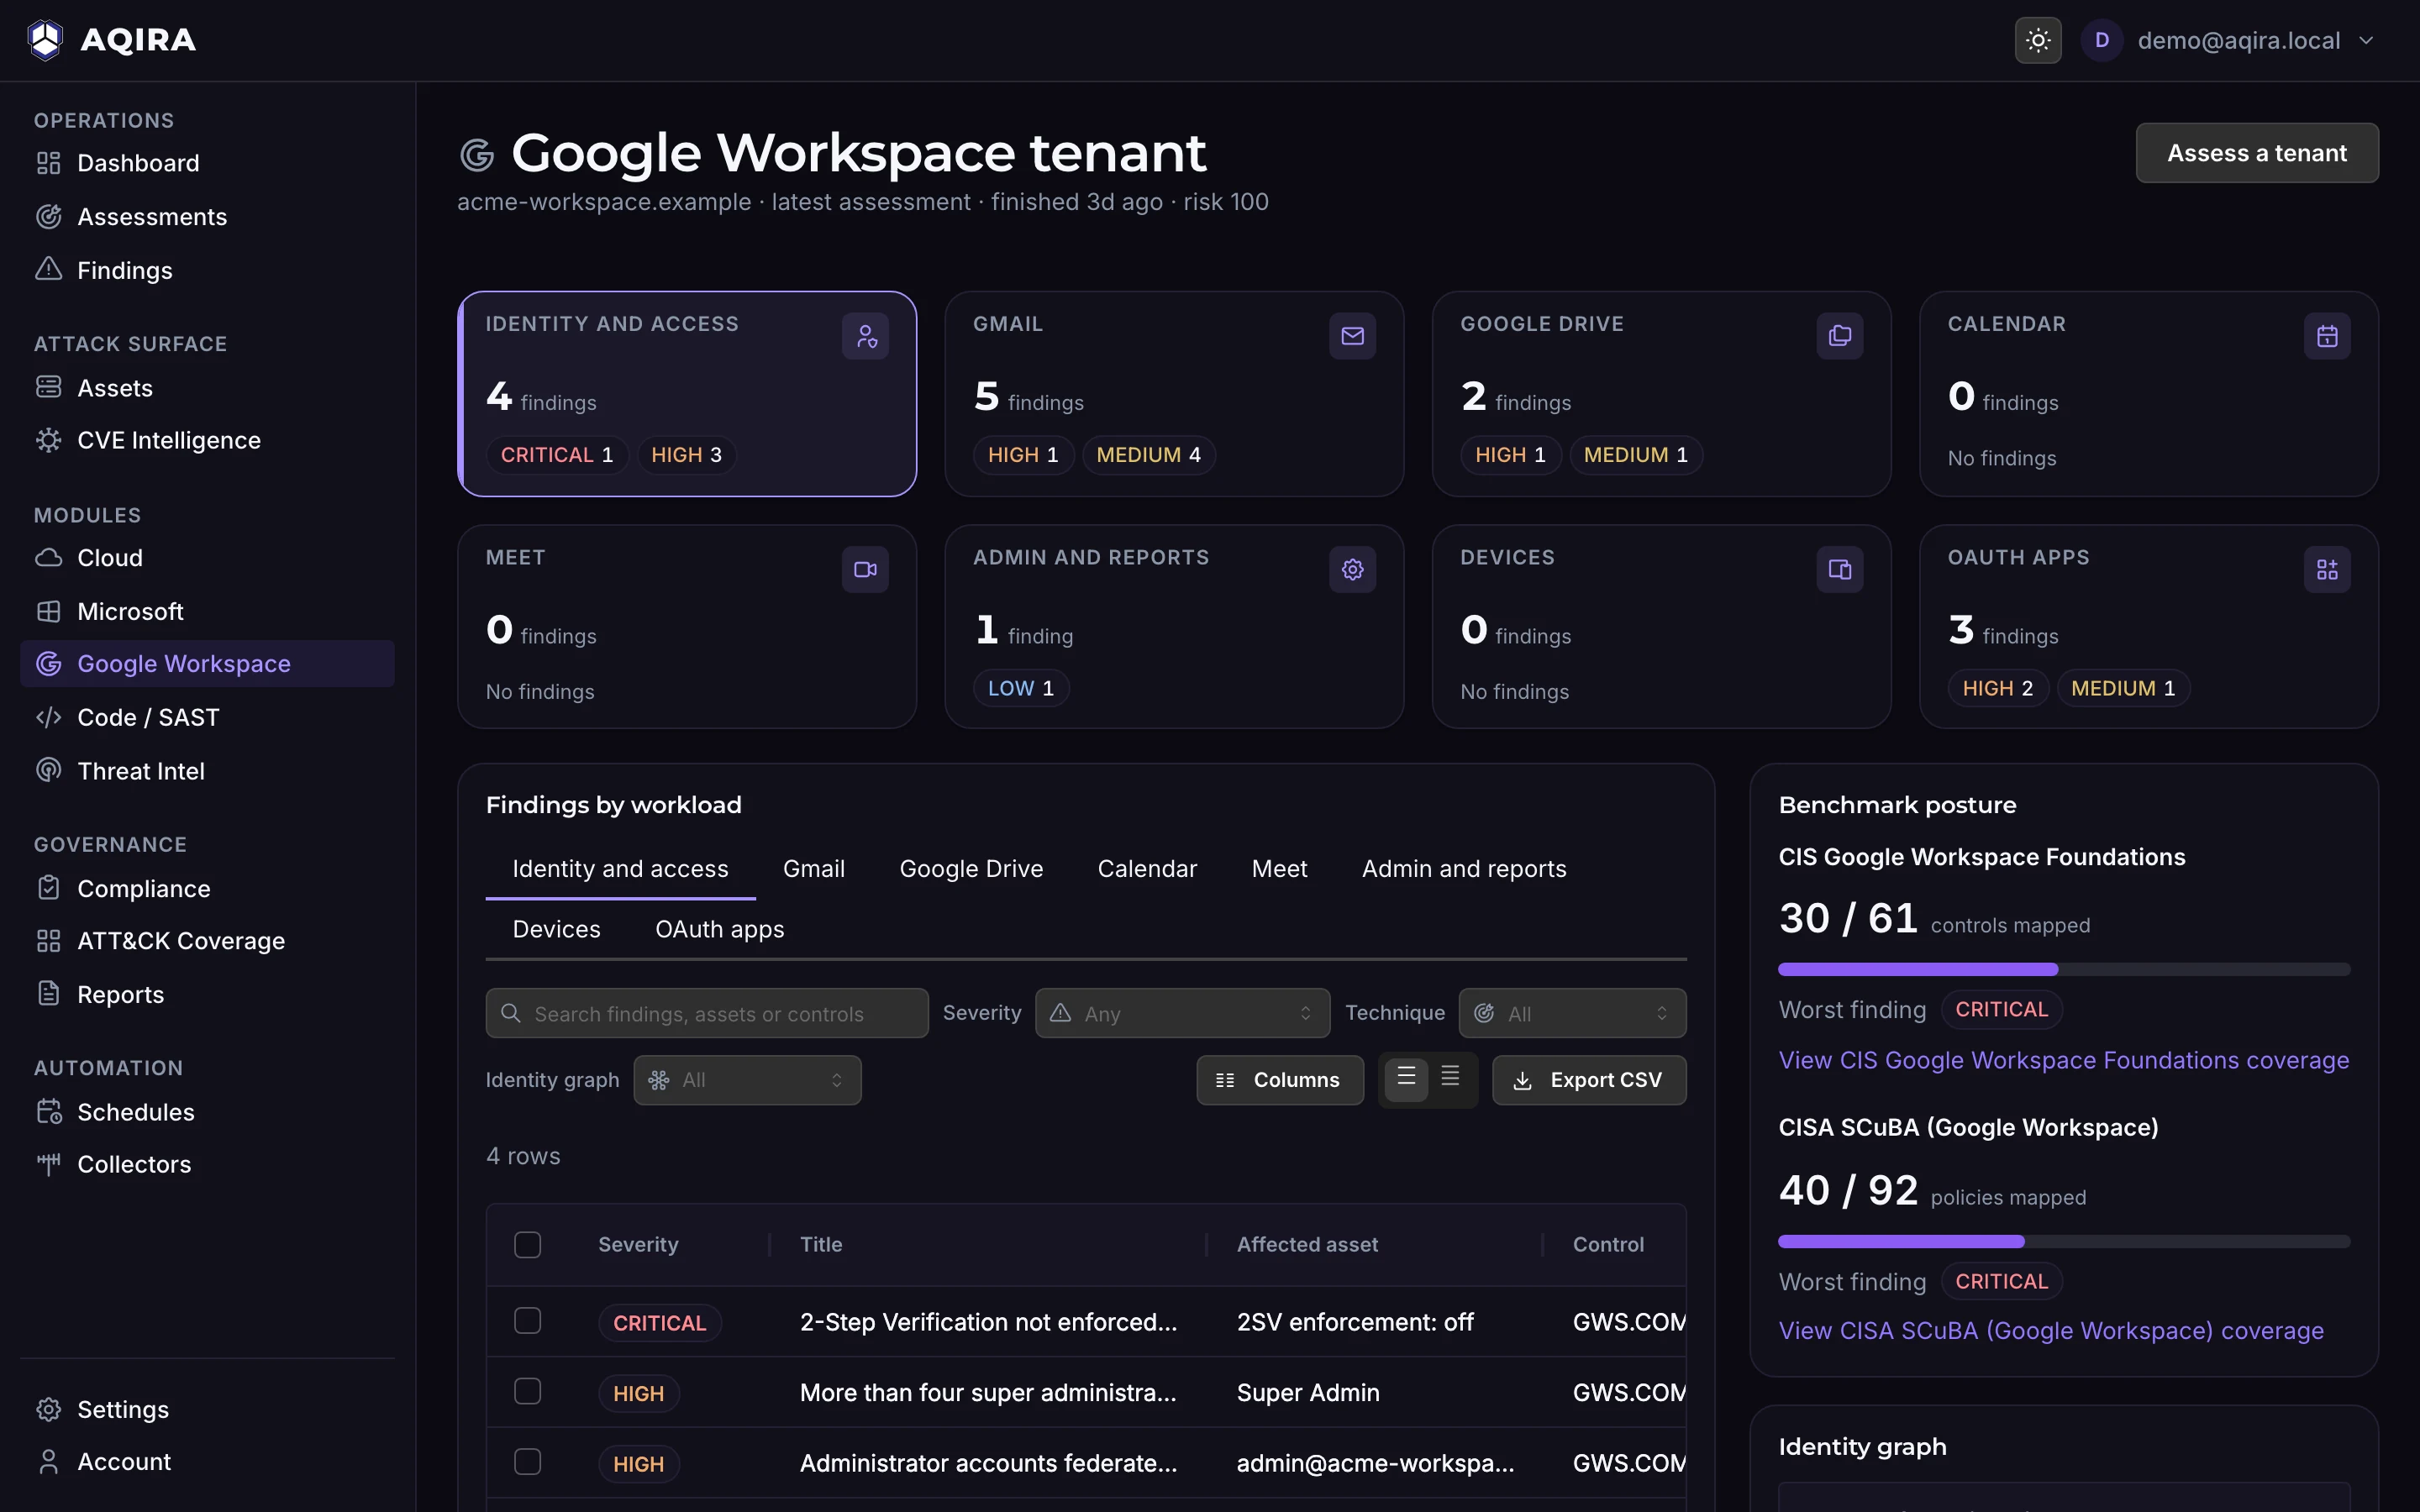
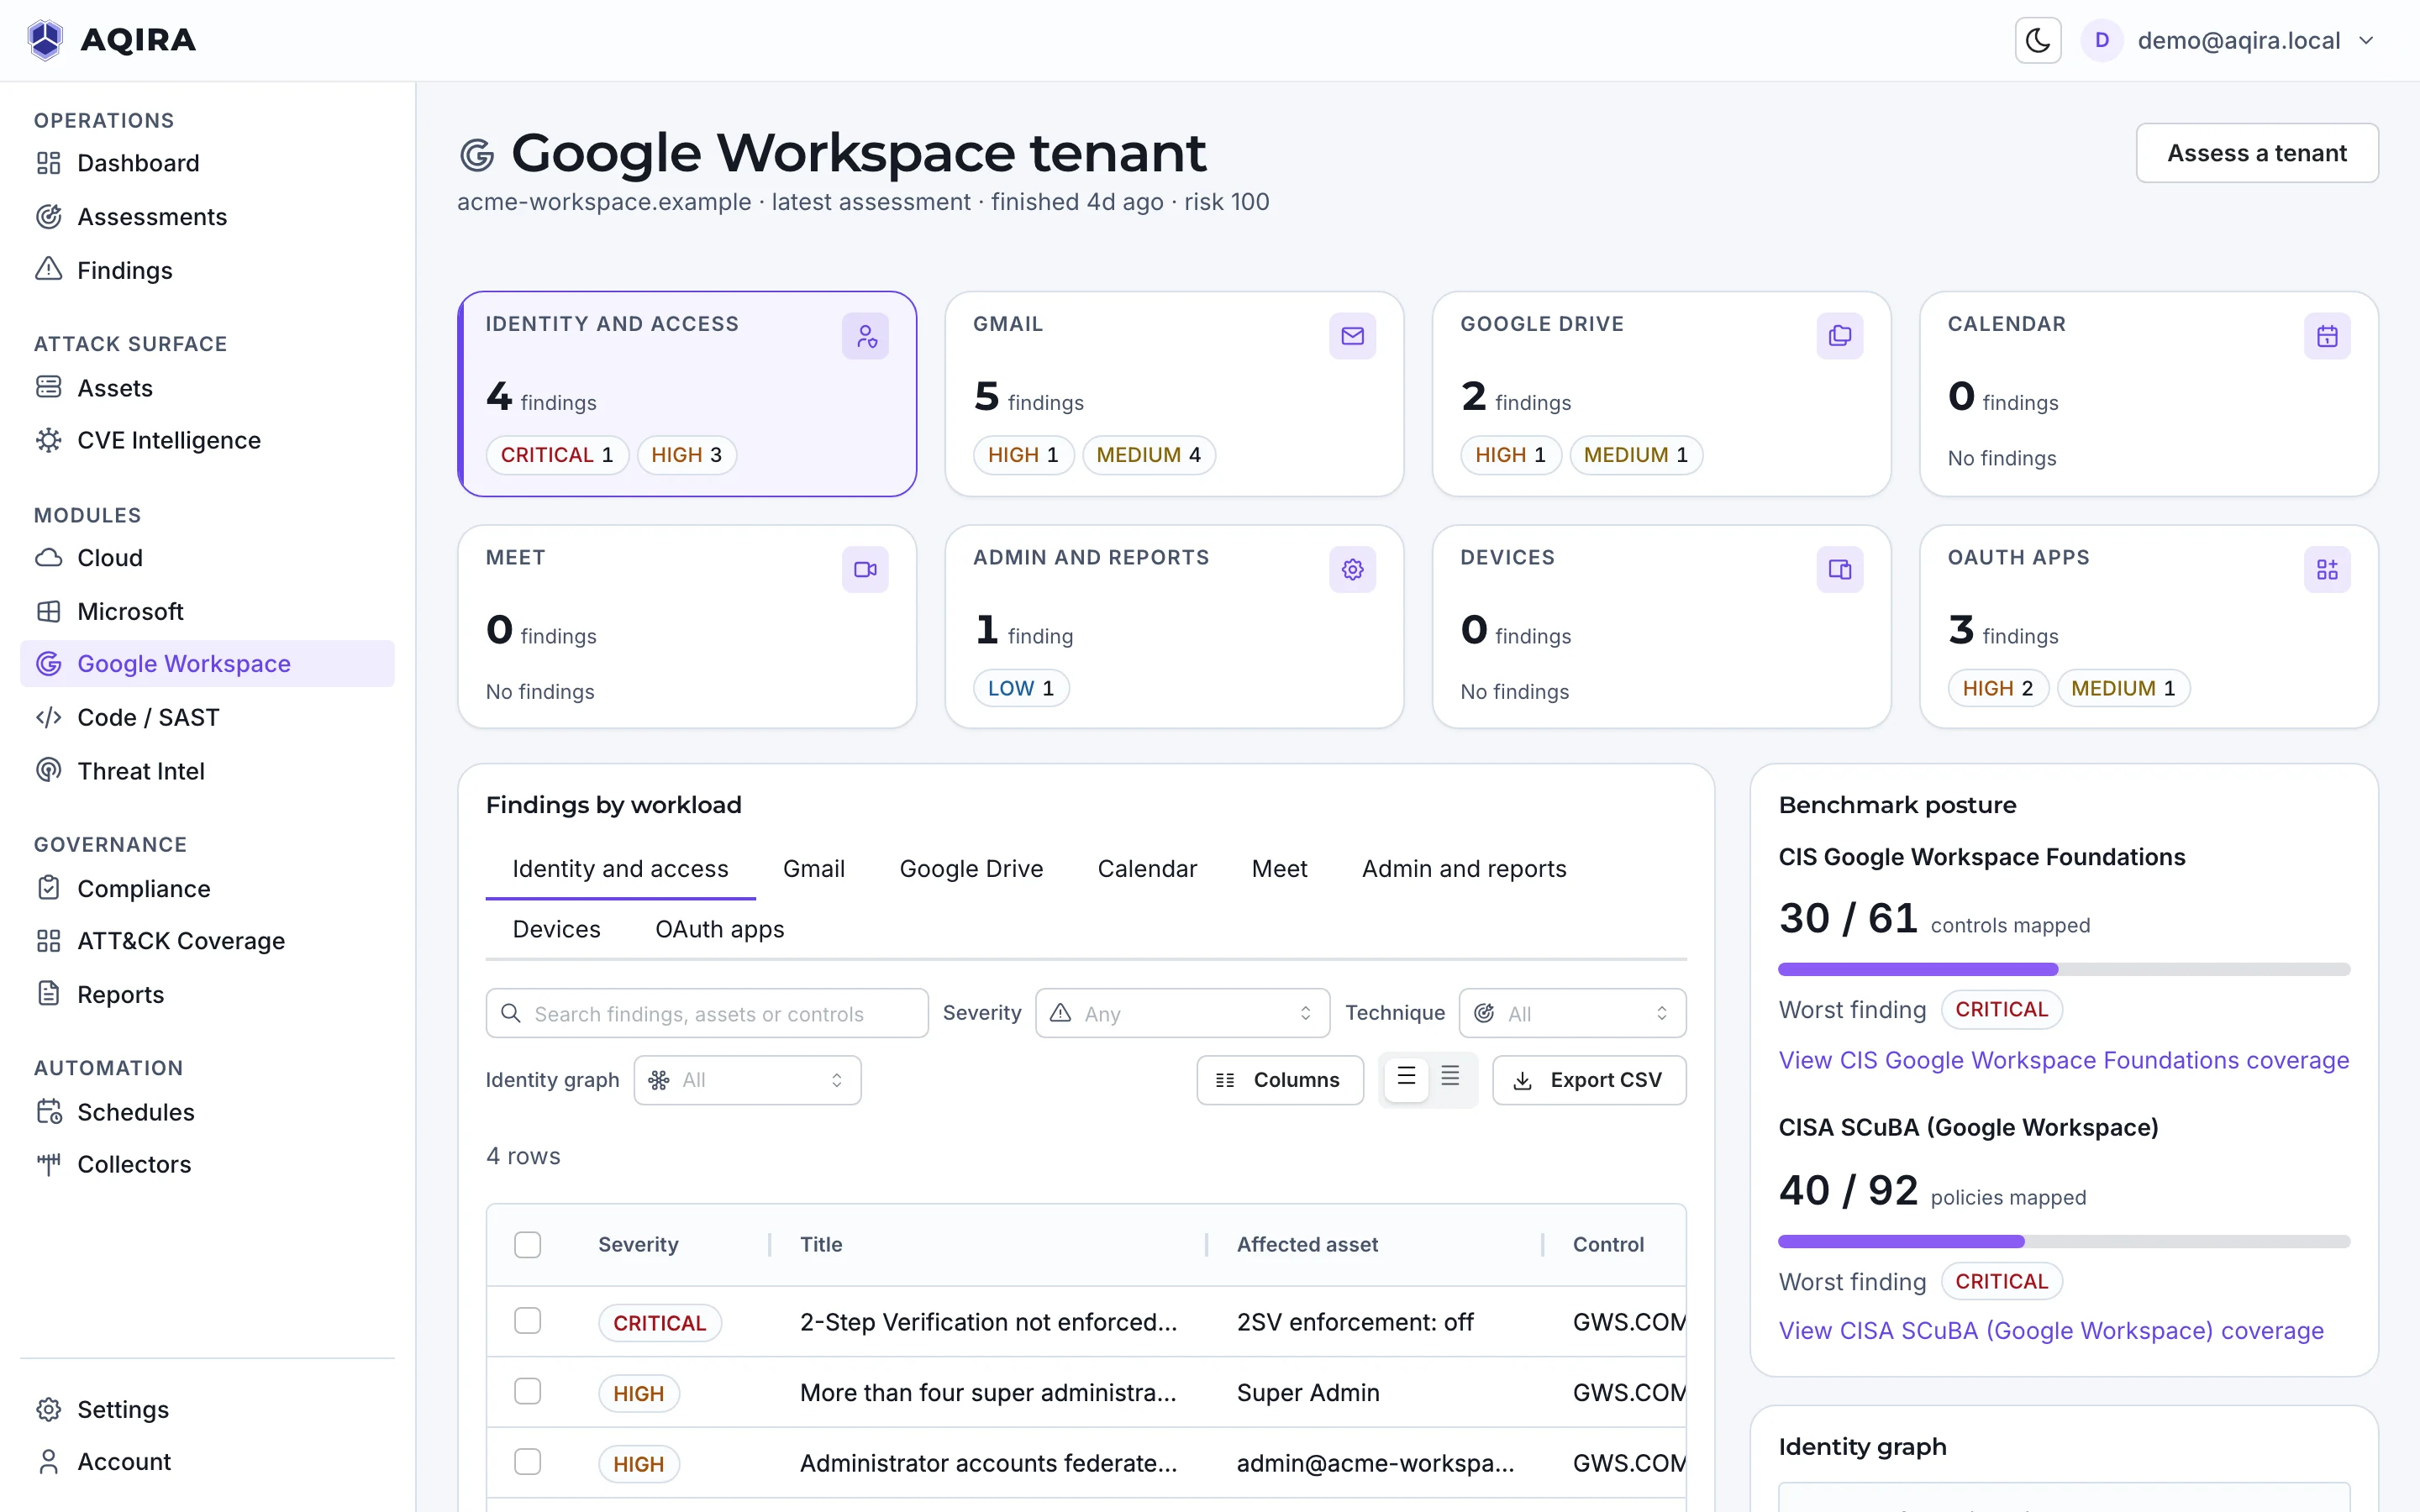
Examples only. What an assessment finds depends on your target; the capture shows a demo assessment.
What it maps, and where results land
Results also land on the Google Workspace screen: findings per workload, sign-in to OAuth apps, and posture against CIS Google Workspace and CISA SCuBA.
- Identities and roles
- Organisational units, users, groups, admin roles and the OAuth apps people have connected.
- Policies and settings
- Sign-in and 2-Step Verification, Gmail, Drive sharing, app access, Marketplace and audit settings.
Mapped to what your auditors read
POLARIS maps every finding to the controls it touches, in every framework that applies.
Scored against
- CIS Google Workspace
- CISA SCuBA (GWS)
Every finding is also mapped to
ATT&CK, OWASP, NIST CSF, NIST SP 800-53, NIST SP 800-171 and COBIT.
Control status, owner and evidence are in compliance mapping; what reaches the client is in the reports.
Where this assessment stops
A clean result covers only what AQIRA tests on a Workspace tenant.
Read-only scopes you delegate
Read-only admin scopes, delegated to a service account in your own admin console; that consent also authorises the assessment.
Settings, not people
It reads how the tenant is configured. It does not phish or test your users.
One intensity
Workspace assessments run at Standard: reading configuration and validating sharing and forwarding to benign proof.
Limits common to every input, and how proof stays benign, are in the methodology.
The other five inputs
Next step
A demo assessment of a Workspace tenant
A demo runs one assessment in the console, with demo data: the agents at work, the evidence behind each finding, and the report.